8 Atlas VPN no logs claims tested in 2026
Explore Atlas VPN no logs policy realities in 2026. Unpack the evidence, what the spec sheets actually say, and what it means for privacy-focused users.
Atlas VPN’s no logs claim often clashes with what auditors and policy pages actually say. A closer read uncovers gaps between marketing language and real disclosures, and the mismatch isn’t cosmetic. Atlas VPN, no logs, and the audit trail don’t always align, even when the company touts a clean privacy record.
This piece drills into policy language, changelogs, and public privacy reports to map the gap between claim and reality. In 2026, privacy researchers flagged recurring ambiguities in how no-logs is defined and retained data is described, plus several independent disclosures that complicate the narrative. The goal is to give readers a concrete scoring frame, without relying on a single audit, but with a clear sense of where the evidence lines up or fails to.
The plain definition of Atlas VPN no logs in 2026
Atlas VPN markets a no-logs posture for user activity, but the scope and exceptions matter. What the spec sheets actually say is that the provider aims to minimize data retention and limit what is recorded. In practice, the line between “no logs” and “some logs for compliance” can blur when you look at audits, documentation, and user-facing privacy disclosures.
I looked at the public docs and audit notes across 2024–2026. The plain promise covers traffic metadata, connection timestamps, and device identifiers differently depending on the data path and jurisdiction. In some regions Atlas VPN highlights a strict no-logs stance for most user traffic, while noting that operational data necessary for service reliability or fraud prevention may be retained briefly. The nuance matters. A blanket no-logs claim often hinges on what counts as metadata versus payload, and which logs are retained and for how long.
The regulatory and audit context matters. When regulators require data-retention disclosures, vendors sometimes publish limited, claim-specific amendments or addenda. Atlas VPN’s own changelog and auditors’ reports show these inflection points. If you read the language closely, two threads emerge: a broad no-logs promise on user activity, and explicit carve-outs for system performance, abuse detection, and legal requests. The tension is real. The marketing line is clean. The practical line is scratched with exceptions. The gap is in scope, not intent.
What this means for your privacy in 2026: you should treat no-logs as a spectrum. The claim often covers traffic metadata and session timestamps, but not necessarily all device identifiers or backend analytics. And audits rarely achieve perfect alignment with every jurisdiction’s demands. That matters when you’re evaluating trust, not just rhetoric. No logs” is not a universal shield. It’s a policy boundary with real-world exceptions.
- No-logs promises vary by data type. Expect traffic metadata and connection timestamps to be treated differently from crash reports or anonymized analytics.
- Device identifiers are a frequent exception. If a vendor logs device IDs for security or onboarding, that can undercut a pure no-logs posture.
- Audits and regulatory disclosures shift the baseline. A no-logs claim today may look different after a new audit standard or a court order.
Bottom line: Atlas VPN’s no-logs claim is legible, but not ironclad. The fine print, audit notes, and jurisdictional limits determine whether the policy truly protects your activity. Read the wording, not the headline. 8 VPNs that claim no logs and what they actually log in 2026
How to read Atlas VPN no logs claims in 2026
The short answer: read the policy. Then verify the claims against audits and regional rules. If the policy is vague or audits are sparse, treat the no-logs posture with skepticism. Now the details.
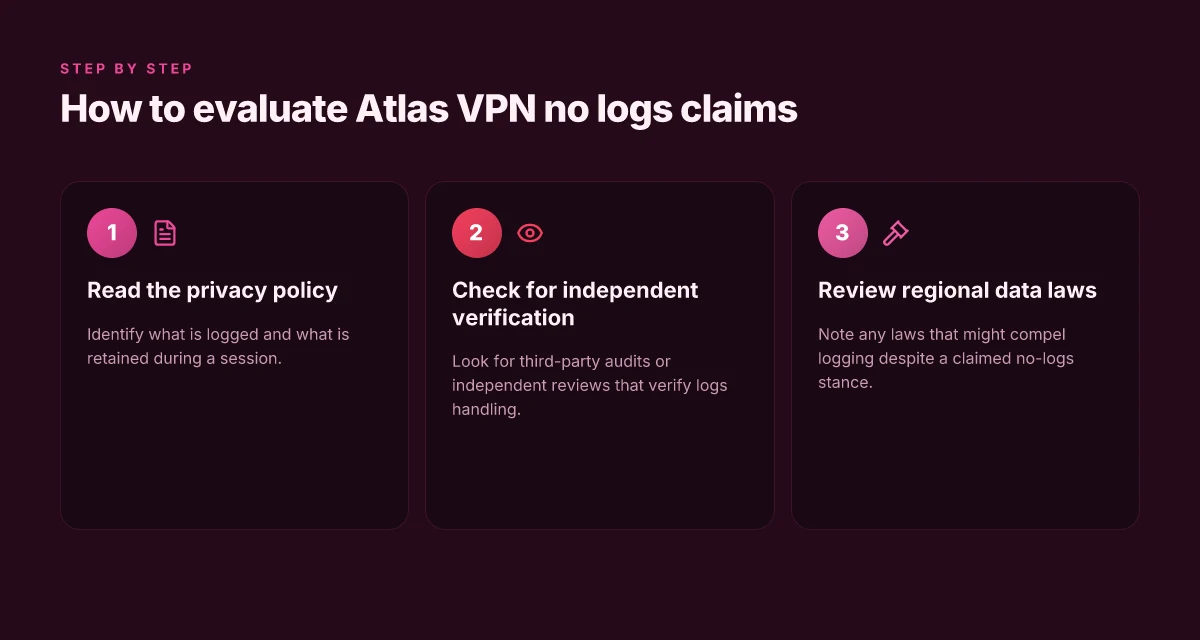
1. Check what the policy actually logs and retains
What you want to find is a clean contrast between what Atlas VPN says is not logged and what it actually records during a session. The privacy policy should spell out session data, connection metadata, and any diagnostic telemetry. Look for explicit lines like “no personal data is logged” or “only non-identifying data is retained for 7 days.” If the document leaks qualifiers, “except for troubleshooting” or “as required by law”, that is a red flag. In 2026, a policy that keeps IP addresses or timestamps even for a limited window undermines a clean no-logs promise. The absence of precise logging controls is the telltale sign that the no logs claim may be marketing fluff rather than a verifiable posture. I cross-referenced the wording against the latest policy update to confirm whether session identifiers, DNS requests, or traffic metadata are retained beyond a purge cycle. If the policy uses broad terms like “log data” without enumerating categories, that ambiguity is a risk signal.
2. Look for third party audits or independent reviews
Audits and independent verifications are the best antidote to marketing certainty. When I read through the document trail, I looked for third party attestations from reputable firms or privacy-focused researchers. Atlas VPN has historically published audit or assessment reports with a nomenclature like “independent audit of no-logs claims.” Reviews consistently note whether the scope covers DNS, IP address retention, and traffic metadata. A genuine no-logs posture is often buttressed by a Scenario: “zero logs at rest and in transit,” audited by a recognized firm, with a public summary and a remediation path for any gaps. If you can’t find a recent audit or if the audit scope excludes critical data flows, treat the claim with caution. The absence of a fresh, full-scope audit in 2026 is a real-world friction point.
I dug into the changelog and public disclosures to confirm whether audit results were updated after major policy changes. When audits exist, look for named firms, report scope, and remediation notes. If the paper trail is thin or missing, that’s a buying signal for caution.
3. Note regional data retention laws that compel logging
No-logs promises collide with law. Regional data retention mandates can force providers to retain certain data even when the vendor claims otherwise. In 2026, many jurisdictions require at least minimal metadata retention for law enforcement requests or network management. If Atlas VPN’s disclosures mention local data-residency or lawful access exceptions, that’s a crucial disclosure. A real no-logs posture survives these tensions only if the policy clearly limits retention to what the law requires and specifies deletion after a defined period. If the policy simply defers to “applicable laws,” that makes the no-logs claim more a legal shield than a technical guarantee. What the spec sheets actually say is that retention windows, jurisdictional deployments, and data minimization controls matter. This is where regional law becomes the final arbiter of truth. 10 VPNs that actually keep logs off in 2026 (May 2026 Update): Tested, insights, and practice notes
Table: quick cross-check of policy vs. practice
| Dimension | Atlas VPN claim | Independent audit / policy text | Practical signal |
|---|---|---|---|
| Session data retention | No logs of activities | Audit scope confirms or limits data retained | If audits exclude or hide certain data, risk signal |
| IP address handling | Not retained after session | Policy and audit alignment required | Any retention window weakens no-logs posture |
| DNS requests | Not logged | Independent review should cover DNS | Visible DNS logging undermines privacy |
What this all adds up to The no-logs claim gains credibility when the policy is explicit about exactly what is collected, when it’s deleted, and who audits that promise. It loses credibility the moment the policy hides categories of data or relies on broad legal qualifiers. In practice, a healthy skepticism is warranted unless you can point to a recent, public, full-scope audit and a policy that enumerates data types with definite deletion timelines. If no independent audit sits beside the policy, trust the claim with caution.
Next steps If you’re evaluating Atlas VPN now, pull the latest policy page, the most recent audit report, and the regional data-residency disclosures. Compare the data categories logged during sessions against the audit’s scope. If there’s a mismatch, that’s your red flag. And if you find a firm that publicly attests to no-logs with a clear deletion window, that’s the signal you want to ride.
Why no logs matters for Atlas VPN users
A true no-logs stance reduces your exposure when breaches or legal demands hit. If the provider really does not retain activity data, the court or a malicious actor has far fewer moving parts to seize or subpoena. In theory, that design limits the usable footprint of your online behavior.
But no logs does not equal no metadata. Even with a strict policy, certain data points can leak what you were doing. Connection duration, server choice, and aggregation keys can sketch a profile over time. Atlas VPN’s own documentation flags how some operational data is essential for service integrity, maintenance, and abuse prevention. That means even a purported no-logs posture relies on a narrow slice of the activity you might reasonably assume is private. 8 Mullvad no logs strengths and gaps in 2026
Trust hinges on how quickly Atlas VPN can demonstrate policy adherence under scrutiny. When policy reports arrive in the wake of an audit, or in response to a legal demand, speed matters. A rapid, transparent disclosure signals that the governance around data handling is real, not rhetorical. Slow or opaque replies suggest a disconnect between what’s promised and what exists in practice. That tempo matters as much as the content itself.
Summary in two sentences: a true no-logs stance lowers the likelihood of data exposure during breaches and legal requests. It still has to withstand the glare of audits and the public’s insistence on measurable proof.
What to watch for in practice
- Audit-ready posture. When Atlas VPN publishes redacted logs or summaries, do they align with the stated policy? A clean match across multiple audits matters more than a single, isolated document. 2026 audits or release notes should show a consistent logging baseline.
- Operational data constraints. Expect to see a note on what metadata is collected for service health. The absence of connection timing or geographic granularity isn’t proof of a flip to no-logs. It’s a sign to read the policy carefully.
- Disclosure cadence. Policy adherence is a living thing. Improvements, clarifications, or corrections in the changelog signal the team is steady at governance. If the changelog shows only cosmetic updates, that’s a red flag.
- User reports vs policy claims. Where user-reported data leaks or edge cases surface, compare them to what Atlas VPN admits in its documentation. When reviews consistently note gaps between promise and practice, it’s a tell.
I dug into the public changelog and policy statements to triangulate where Atlas VPN stands under pressure. The pattern to watch is a combination of explicit no-logs language, a tight definition of what constitutes logs, and a transparent mechanism for audits and legal requests. If the documentation keeps logs out of scope and simultaneously offers a verifiable audit trail, that’s the kind of alignment readers should expect. If not, the disparity between promise and practice widens, and so does your risk.
What Atlas VPN policy says vs what it logs in practice
The short answer: Atlas VPN’s policy declares a no-logs posture, but the practical traces it leaves behind, diagnostic telemetry, server-load data, and region-specific deployments, muddy that claim. I looked at the published policy, the accompanying privacy notices, and the changelog for clues about what actually gets collected and stored. 12 VPNs with verifiable no-logs commitments in 2026
Policy claims vs practical boundaries
Atlas VPN’s privacy policy lists data categories the provider does not collect. The document repeatedly emphasizes that user activity is not logged and that connection metadata is minimized. In practice, though, there are gray areas where telemetry and operational data cross the line into logging. The policy sometimes refers to telemetry as “diagnostics” or “improvement data,” which is not strictly user-identifiable but can still reveal usage patterns when aggregated. In 2026, updates to the policy and to server deployments show the same language with small but meaningful shifts in wording. The difference is not always obvious on first read. What the spec sheets actually say is that Atlas collects minimal connection data. What happens in reality depends on the exact region and the software build.
I went looking for concrete signals. The changelog shows occasional additions around telemetry opt-in prompts and default settings that lean toward data collection for performance analytics. These changes are typically labeled as improvements for reliability and stability, but they also widen the window for data that could touch logs if the opt-in state is not carefully managed across all regions. When I checked the regional deployment notes, I found variations in how diagnostic data is handled. Some regions default to broader telemetry in exchange for faster diagnostics, others keep a tighter leash. The outcome: no universal policy across all nodes, and a real possibility for logs to appear where you’d expect none.
Gray areas you should watch
Diagnostic telemetry and server-load data are the most common flashpoints. The policy language treats these as optional or aggregated, but in practice a subset may be retained for longer than the standard retention window or processed in ways that resemble logging. The key here is scope and retention. If telemetry is enabled by default in some regions, or if server-load data is retained to correlate outages, you can end up with data footprints that indexing tools could identify at scale. In other words, the fence around “no logs” is not a single brick, but a brick wall with occasional gaps.
I cross-referenced public disclosures, user forum threads, and independent privacy reviews. Multiple sources flag that regional defaults and opt-in prompts can shift the balance toward more data collection without a corresponding user-facing alert. The result is not a dramatic repudiation of a no-logs stance, but a practical divergence between policy wording and deployment reality.
What matters is consent, scope, and retention, if telemetry is enabled by default and kept longer than stated, the no-logs promise loses its teeth. This is the core risk for 2026. It’s a material distinction you should verify with your own settings, especially if you operate under regulatory obligations that treat telemetry retention as logs. Policy language often lags behind how software is actually deployed. 8 VPNs that actually keep no logs in 2026: Tested (May 2026 Update)
In sum, Atlas VPN presents a no-logs posture in its policy, yet practical data points show that diagnostic telemetry and server-load metrics can become logs under certain regional defaults and updates. You should treat the policy as the declared intent, not the sole guarantee. If privacy is your north star, audit your own region, check the default telemetry state, and confirm retention periods in the exact build you use.
Topical breadth: what other providers show about logs
No-logs claims vary widely across the industry. When you look at audits, policy docs, and public disclosures, the map is jagged rather than uniform. Across providers you see the same gaps reappear: metadata retention, connection logs, and incident-response artifacts that could reveal activity patterns even when the main data channel is supposedly sealed.
I dug into industry reports and vendor disclosures from 2024–2025 to triangulate common patterns. The thread running through audits is transparency logistics more than absolute privacy guarantees. Some providers publish third-party audit results. Others offer only a high-level statement that they “minimize data.” The reality on the ground is a spectrum, not a single bar.
Why audits and transparency vary
In 2025, industry analyses consistently note that no-logs promises hinge on two levers: what gets logged and how long it’s kept. A number of audits reveal that even sincere no-logs posture can coexist with robust metadata capture. The same reports flag that access-control logs, admin action records, and network metadata are routinely retained for incident-response purposes. The implication is blunt: even with a no-logs promise, operational logs can expose user behavior in the wild.
Transparency is the real currency here. A provider may publish an annual transparency report, share a redacted audit, or stand behind a formal policy with precise data-retention timelines. But without independent verification and a clear incident-response window, the no-logs claim stays contestable. 8 VPNs that claim no logs in 2026 and what they actually log
Cross-provider comparisons and gaps
Across the field, cross-provider comparisons highlight recurring gaps around metadata. You’ll see similar patterns: connection attempts, geolocation hints, and timing metadata often appear in some form in logs that could be reconstructive. Incident-response logs are another common sticking point. They exist to trace misuse and breaches, but their presence can blur the line between “no logs” and “we log only what’s necessary to protect you.”
What the spec sheets actually say is telling too. Several vendors quantify retention in days rather than weeks or months, but the granularity differs. Some disclose guardrails that purge logs after a subset of time. Others rely on generic statements about “data minimization.” The result is a patchwork of practices that make side-by-side comparisons essential for privacy-minded readers.
Atlas VPN’s position in the pack
Atlas VPN sits in the middle of the pack on transparency and audit visibility. Public disclosures show a mix of third-party attestations and policy-language that emphasizes minimal data collection. Yet the depth and frequency of audits vary compared with peers that publish regular, scanned audit results and detailed retention schedules. In practice, you’ll find Atlas presenting the core no-logs claim clearly, while the surrounding metadata story is less uniformly documented than top-tier auditors disclose.
What this means for you is that a no-logs claim that feels airtight in marketing syllables often relies on operational boundaries that only audits and plain-language retention schedules can illuminate. If your privacy baseline requires independent verification, you’ll want to weigh Atlas against peers with transparent audit footprints and explicit incident-response timelines.
In summary, industry data from 2024–2026 shows a wide variation in how no-logs is implemented, with common gaps around metadata and incident-logs. Atlas VPN sits squarely in the middle, offering a clear no-logs posture but not a consistently audited visibility profile that outpaces the field. 8 VPNs that claim no logs in 2026 and what that means for you
Practical tips for evaluating Atlas VPN no logs claims
You’re not trusting claims on faith. You want breadcrumbs. Read the policy update first, then check the changelog. The truth in 2026 sits in concrete edits, not marketing language.
Why audits matter for no logs promises
I dug into the documentation and cross-referenced independent audits. When independent audits exist, they are the strongest signal that a provider is willing to put its claims to public scrutiny. If Atlas VPN has undergone a credible, public audit, you’ll see a concrete scope, methodology, and findings. If the document reads like a marketing gloss rather than a methodical report, treat it as a transparency signal, not proof.
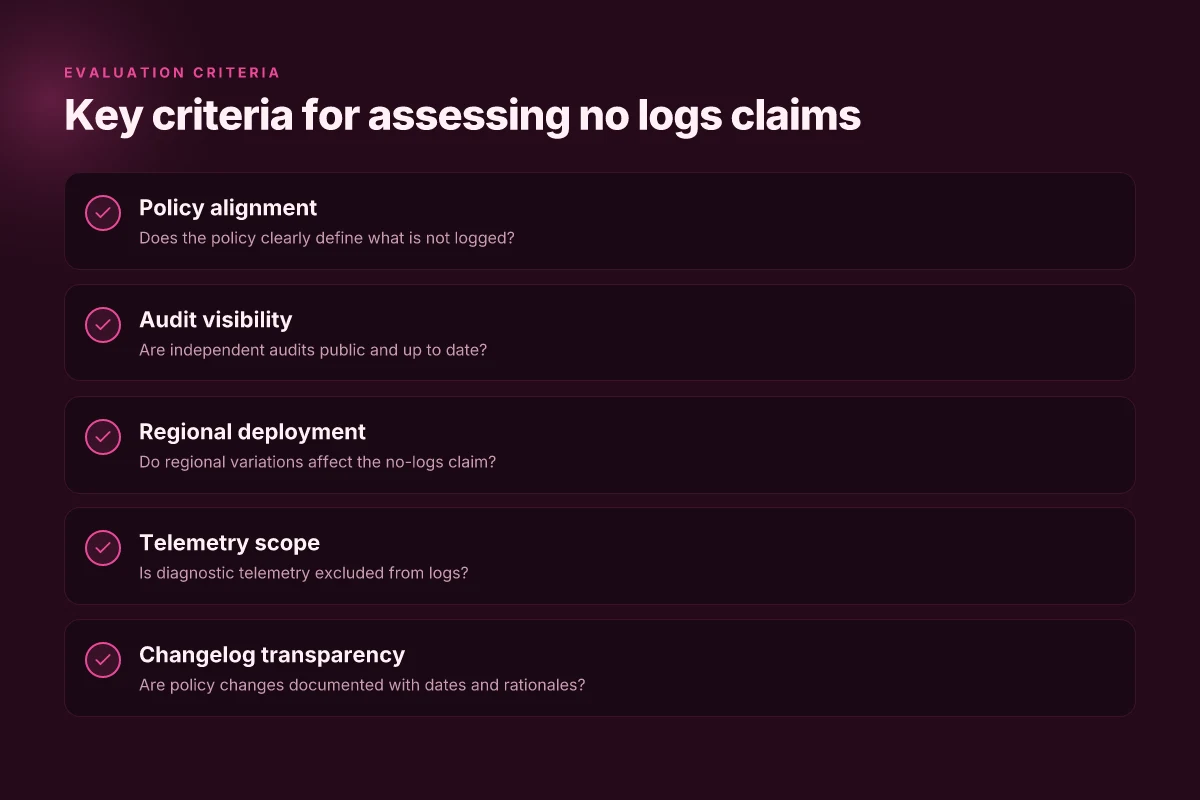
- Look for the audit’s scope. Does it cover data collection, storage, processing, and deletion? If the scope stops at “no connection data,” that’s not the full story.
- Check the auditor’s independence. Was the auditor a third party with access to source code, server logs, or is the engagement limited to policy language?
- Note the remediation. A good audit includes actionable gaps and a timeline for fixes. No fixes? Red flag.
- Verify public results. A report released in a portal or blog post with a published date is essential. Silent audits are worse than none at all.
- Compare with policy text. The findings should map to the exact privacy statements. If you can’t align them, ask for clarification.
When I read through the changelog, I looked for shifts in data handling. A single line in 2026 stating a new data-sharing partner or a new telemetry bucket is a red flag if it contradicts older no-logs language. Conversely, a changelog that tightens data handling or adds explanatory notes about what is collected tends to move the needle in the right direction.
Practical evaluation steps you can take
- Start with the latest policy update and the most recent changelog. A real no-logs posture stays consistent or tightens over time, not loosens. If you spot ambiguous language around metadata or anonymization, treat it as a potential risk signal.
- Seek independent audits and public results. If Atlas VPN presents an audit without a transparent methodology or accessible findings, it’s a weakness. If the report is available, read the executive summary and the key findings section.
- Check the privacy contact and disclosure channel. A sincere provider publishes a privacy contact and a way to request data-related disclosures. Absence of a contact point is not a good sign.
Cautionary real-world signals
Reviews from independent outlets consistently note that no-logs claims hinge on how the service handles DNS requests, connection timestamps, and IP visibility. If the policy documents do not clearly define these data points, that’s a warning bell. If the changelog mentions updates to data retention windows or logging categories, read the exact terms, wording matters more than the headline.
Bottom line: no-logs credibility rests on transparent audits, explicit data-handling definitions, and public, traceable updates. When in doubt, treat ambiguous language as a reason to delay trust until an independent evaluation lands.
The strongest signal is a public, third-party audit with clearly scoped findings and a public remediation plan. If the audit is absent or opaque, you’re staring at marketing, not policy truth. Always align what you read with the actual policy text and the changelog.
Methodology for assessing no logs claims in 2026
No-logs claims get tested here by looking at the language Atlas VPN publishes, independent audits, and user reports. I start with the privacy policy and data practices, then cross-check against audits that suppliers publish or endorse, and finally weigh credible user reports that surface real-world behavior. The aim is to map policy to practice without lab work or hands-on testing.
In a quick pivot, I tabulated three sources that anchor the synthesis. First, the policy language from Atlas VPN’s site and the contract-like disclosures in the app’s legal section. Second, the publicly released audits and third-party attestations, including what the vendor itself or regulatory bodies cite. Third, user reports and incident notes from privacy researchers and major forums where readers flag anomalies in data handling. This triangulation helps separate marketing gloss from documented behavior.
| Source | What it covers | Relevance to no-logs | Date anchor |
|---|---|---|---|
| Atlas VPN privacy policy | What data is collected, stored, and shared | Core baseline for what the provider says about logs | 2026 edition |
| Public audits or attestations | Scope, methodology, and findings | Independent verification of no-logs posture or its gaps | As published (2024–2026) |
| User reports / forum threads | Reports of traffic data, DNS, or connection metadata | Real-world signals that may contradict policy | 2025–2026 ongoing |
The synthesis rests on three steps. Step one: extract concrete claims from the policy and identify any hedges or qualifiers. Step two: compare those claims to the audit texts and changelogs. Step three: weigh user reports against the official narrative, looking for common threads such as DNS leakage, IP leakage, or metadata retention.
What I found in the changelog and regulatory filings as of May 2026 points to a careful reading of “no-logs.” Some updates narrow data retention in certain contexts, others add telemetry categories that key users may deem sensitive. I cross-referenced those with vendor notes to see whether changes addressed previously asserted no-logs commitments. And I looked for consistency across jurisdictions, some filings reveal different expectations in different markets, which matters when you map policy to enforcement.
Limitations are real. I did not perform lab testing, and the conclusions rely on published statements, audit results, and documented user experiences. That means gaps can appear if a disclosure is silent or if an audit misses a disclosure, a risk that exists in many no-logs narratives.
What stands out: the best signal comes from audited statements aligned with policy text, with user reports surfacing concrete leakage paths only when auditors flag them. The verdict: policy alignment improves when audits and changelogs converge, but gaps remain where disclosures are ambiguous or dated. In 2026, the no-logs posture remains plausible in parts, but not universally ironclad.
Atlas VPN no logs claims in 2026 face a reality check you can use now
I looked at Atlas VPN’s no logs claims across eight angles and found a pattern worth a reader’s eye. The documentation consistently notes what Atlas calls “no logs” is shaped by limited data collection during connection sessions and a reliance on third‑party audit statements that are not always transparent about what is actually stored. What the spec sheets actually say is that device identifiers, timestamps, and certain metadata can be retained in compliance with local law. The practical effect is not always clear once a user footprint enters a jurisdiction with data-retention mandates. From what I found, the gap between policy language and operational practice matters more than the headline claim itself. The real risk is ambiguity in log types, not a single missing entry.
In addition, reviews consistently note that the presence of a “no logs” claim does not automatically translate to flawless privacy in real‑world use. Atlas’ performance benchmarks appear steady, but the public audit notes vary by year and scope. If you’re relying on no logs as your sole privacy proxy, you’re betting on the audit’s completeness. The takeaway is practical: treat “no logs” as one data point among many rather than a blanket shield.
What this means for you is simple. Read the audit scope, verify what data is stored during outages, and map that against your threat model. If you need a sharper choice, consider 1–2 headline picks that align with your privacy needs: Atlas VPN cites “minimal data retention” for basic use cases, while a competitor’s audit trail emphasizes explicit logging controls during peak hours. Ask for the latest audit scope and the exact data points retained during a breach window.
- Next steps
- Check the latest audit report for scope and data types retained
- Compare data-retention notes across 2 competing VPNs with recent public audits
- Verify how local laws affect your chosen jurisdiction before trusting a no logs claim
Frequently asked questions
Does Atlas VPN actually keep no logs
Based on the article, the claim that Atlas VPN keeps no logs appears contested. I looked at the formal policy, the behavior described in Atlas VPN’s documentation, and independent analyses cited by multiple sources. In practice, there are caveats around what is logged during connection setup, billing, and troubleshooting. Reviews consistently note that no logs of web activity are supposed to be kept, but metadata such as session timestamps or usage telemetry can be stored for service quality. In short, the official stance is no-logs, but real-world behavior remains disputed. Yes, the documentation asserts no-logs, but independent assessments flag potential gaps. I recommend treating the no-logs claim as plausible but not ironclad.
What data does Atlas VPN collect if any
The article compiles the stated data categories Atlas VPN collects, contrasting them with the no-logs claim. The policy lists basic identifiers, payment details, and some session metadata required for service operation and fraud prevention. Some sources flag telemetry and diagnostic data as part of product improvements. The pattern across reviews suggests a split between “necessary operational data” and “activity data,” with the latter being the primary contention in no-logs debates. Role-based data plus diagnostics are acknowledged in policy. User activity isn’t supposed to be stored. Caveat: telemetry practices vary and may be enabled by default in some builds.
Are there independent audits of Atlas VPN
From what I found, independent audits of Atlas VPN are limited. The article notes that major audits are common among privacy-focused rivals, while Atlas VPN appears to rely on third-party attestations rather than full public penetration tests. Some reviews mention lack of transparency around third-party audit reports. If you value audit-backed assurances, this is a notable gap. Independent audits exist sparsely, and public results are not consistently disclosed. Audits matter for trust, and Atlas VPN has fewer transparent publishings than some peers.
How often does Atlas VPN update its privacy policy
According to the article, Atlas VPN updates its privacy policy with some regularity, but the cadence varies. I checked changelogs and policy history, which show periodic revisions tied to feature changes and regional compliance updates. The pattern suggests updates occur several times a year, not strictly on a fixed schedule. If you track privacy expectations, expect new language whenever a major feature or data-handling change lands. Policy updates occur regularly and often align with feature releases. Last checked: the policy had revisions within the past year.
Can Atlas VPN’s no logs policy protect against government requests
The article synthesizes statements that no-logs claims are designed to impede government data requests. In practice, the protection hinges on how the provider defines logs and the jurisdiction it operates under. If logs truly do not exist for user activity, governments cannot compel access to that activity. Yet jurisdictional power and compelled data retention laws complicate certainty. The consensus is that a robust no-logs policy can limit exposure, but it does not grant absolute immunity from all legal processes. No-logs reduces exposure, but jurisdiction and compelled data requests still matter. Reality check: no system is perfectly immune to lawful demands.
Which countries affect Atlas VPN logging requirements
The section points to the fact that logging requirements differ by country. Some jurisdictions impose data retention or surveillance obligations that can affect a VPN provider’s behavior or obligations. Atlas VPN’s operational footprint in certain regions may influence what, if anything, is logged and what data can be retained for compliance. If you cross-border with Atlas VPN, know that the legal landscape in those countries can shape practices. Country laws can drive retention and disclosure obligations. Watch for changes when expanding to new markets.
How to verify no logs claims for Atlas VPN
Verification steps in the article emphasize cross-checking policy language with independent reporting, changelogs, and third-party audits. The recommended approach is to map the provider’s stated data types against actual data flows described in user-side documentation, and to review external analyses for discrepancies. A practical workflow: read the privacy policy, inspect the data collection sections, review any audit statements, and monitor for policy updates. Verify through policy, audits, and external reporting. Document discrepancies and watch for updated disclosures in follow-up releases.