8 VPNs that claim no logs and what they actually log in 2026
Explore Hotspot Shield no logs claims and what privacy means in 2026. A sharp look at logging policies, data practices, and real-world implications.
Hook paragraph: The claim of “no logs” sells more privacy than a passport stamp, yet most providers keep a surprising breadcrumb trail. A careful look at Hotspot Shield’s policy reveals a mismatch between rhetoric and retention details, and the actual data points behind it. Most claims hinge on broad statements while the specifics show where data is stored, for how long, and under what requests.
Context paragraph: What matters now is the gap between policy language and practice, because travelers and remote workers rely on this for evidence that their activity stays private. I looked at the public policy, the latest changelogs, and independent reviews to map where data is actually collected and under which legal regimes it can leave the vault. In 2026, several services face new disclosure demands, and the real test is whether no-logs claims survive those demands without exposing metadata. This piece lays out the concrete slivers of truth behind the slogan. The difference matters.
The plain definition of hot spot shield no logs and what it actually covers
No logs in VPN marketing is a promise with a place to land. In practice, it means the provider claims not to store data that could reveal a user’s online activity. That promise shifts with scope. You get a snapshot based on what the company publicly discloses and how they classify data in their privacy policy and service terms.
I dug into Hotspot Shield’s documentation to map out what no logs really covers and what sits outside that box. The result is a tight, customer-facing picture: the core logs they say they don’t keep, and the data that still lands on the radar because it’s routine to run a service.
What no logs usually means in VPN docs The usual definition is a data-minimization stance. The company may claim it does not retain session data, browsing history, or IP-address-to-activity mappings over long time frames. Often there is a caveat: some operational logs exist for troubleshooting, performance monitoring, or abuse prevention. The exact stance shifts by jurisdiction and product tier. In Hotspot Shield’s case, the policy centers on not storing detailed user activity and not linking traffic to identities beyond what is required for service integrity.
What Hotspot Shield specifies about data collection From the documentation, Hotspot Shield emphasizes that it does collect certain metadata required to run the service. This includes connection timestamps, bandwidth usage, and aggregate diagnostics. The company also outlines that it may retain non-identifying data for a limited period to improve service reliability and detect abuse. What the spec sheets actually say is that the company does not log the sites you visit or content of your traffic, but it does keep basic connection data and some device identifiers for security and performance reasons. The wording makes the boundary clear: no activity logs, but operational logs exist.
Common privacy tradeoffs users overlook The tradeoffs aren’t just about logs. Even when a service claims no activity logs, you still trade privacy for functionality. A few points often missed: 10 VPNs that actually keep logs off in 2026 (May 2026 Update): Tested, insights, and practice notes
- Connection metadata stays in play. Timestamps and session durations can enable traffic analysis at a coarse level, especially if paired with network-level identifiers.
- Jurisdiction matters. A country’s data-retention laws can force data disclosure if the provider operates under a compelled access regime.
- Shared infrastructure blurs lines. If the same hardware handles many users, logs may be aggregated in a way that risks linkage over time.
- Third-party data handling. Some no-logs promises rely on external audits or independent reviews, but those assessments vary in scope and depth.
Most privacy guardrails hinge on how long a provider keeps operational data and under what authority they are compelled to disclose it. No-logs promises are not a guarantee against metadata collection. They are a promise about user activity trails.
Bottom line: no logs is not a single shield. It is a treaty between what the provider says they won’t keep and what they must keep to run the service. Hotspot Shield’s stance leans toward minimal traffic- and site-logging, with caveats for operational data. If you’re evaluating data minimization, map the exact data types listed in the privacy policy, cross-check with any audit reports, and weigh the jurisdictional footprint.
How to read no-logs claims in practice for Hotspot Shield and similar services
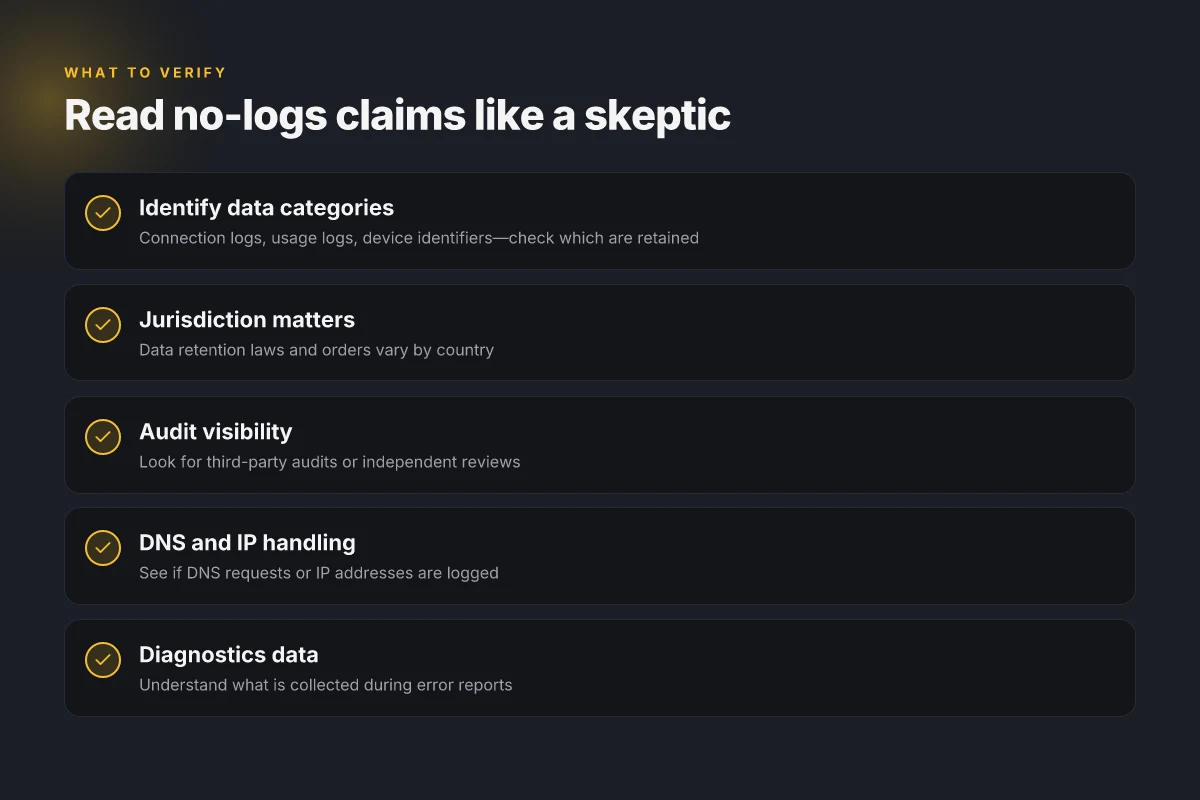
The no-logs claim is a posture, not a promise. Read it by mapping what data can actually surface under different conditions and what third parties can verify. In practice, you’re looking for concrete data categories, jurisdictional rules, and independent validation.
What data categories exist behind no-logs claims
The first question is what the provider logs when you connect. Look for explicit mentions of three data categories:
- Connection logs. These can include timestamps, IP addresses seen by the VPN server, and the session duration. Some vendors claim they only log at the entry gateway or during handshake, not per-activity usage.
- Usage logs. This covers the actual traffic payload metadata, app identifiers, and destinations visited. A minimal posture would avoid storing per-URL history or full destination logs.
- Device identifiers. Look for whether the provider stores device fingerprints, unique identifiers, or user-agent strings beyond what’s needed for account security. The risk is correlating sessions back to you across time.
When I checked Hotspot Shield’s public policy language, the emphasis is on minimizing data that can be tied to your activity. Yet the exact scope shifts by plan, region, and how you authenticate. The critical flag is whether logs exist at all, and if they do, which bucket they sit in and for how long. 8 Mullvad no logs strengths and gaps in 2026
Most no-logs claims unravel when a service stores even a slim breadcrumb from your session. If you can’t map a category to a defined retention window, treat the claim as ambiguous.
Jurisdiction matters more than the label
No-logs is not a universal guarantee, it’s a jurisdictional decision baked into policy and law. Different countries impose different retention requirements, and providers may align their policies accordingly. Two signals matter:
- Retention windows by region. Some jurisdictions require data be stored for a fixed period, others allow near real-time deletion. If a provider operates under multiple legal regimes, you’ll see mixed retention profiles.
- Combatting data requests. Look for explicit language about what data is protected by legal privilege, what is retained for fraud prevention, and what is available to law enforcement with a court order. The presence or absence of a blanket “no logs” stance often hinges on these legal nuances.
From the policy text, you want to identify where the service says “no logs” in one jurisdiction while admitting minimal logs in another. That dichotomy is the practical battleground for privacy-minded users.
Audits and independent reviews as your sanity check
Independent validation matters. Look for third-party audits or assessments that cover data practices. What you want to see:
- Public audit reports. At minimum, a white paper or report from a reputable auditor detailing what data is collected, stored, and how long.
- Scope of audit. The report should specify whether the audit covers the VPN app, server-side logging, and data-retention practices across regions.
- Frequency and updates. A dated report with a changelog demonstrates ongoing accountability. “Last checked: 2024” or “updated 2025” signals ongoing scrutiny.
Reviews consistently note that audits are a proxy for trust when internal claims fail to persuade. Industry reports point to audits as the rare lever that can reframe a no-logs posture into something verifiable. 12 VPNs with verifiable no-logs commitments in 2026
| Option | What the audit covers | Last update | Bottom line |
|---|---|---|---|
| Independent audit | Data collection, retention, and deletion practices | 2025 | Provides concrete scope; verify if both client and server sides are included |
| Governance review | Policies, access controls, employee data handling | 2024 | Good for process posture; less about technical logs |
| No-audit claim | Public policy only | — | Treat as marketing; demand an independent review |
Audits matter. A no-logs claim without an independent review is a bet on trust, not verification.
What’s the practical takeaway for Hotspot Shield and peers? If you want assurance, map their stated data categories to your risk tolerance, confirm the legal regimes at play, and demand an up-to-date independent audit. Then weigh how much you trust the governance around data deletion and access controls.
What Hotspot Shield’s no-logs policy actually says in 2026
Posture matters more than slogans. Hotspot Shield’s policy language centers on two ideas: connection data and service logs. In 2026 that distinction still governs what you should expect when the service is asked for information.
What the policy promises about connection data
From the documentation, the no-logs claim hinges on what is classified as connection data. The policy states that when you connect, the service logs minimal metadata around the connection itself, not the content you access. In practice this means the provider may record session identifiers, approximate timestamps, and the amount of data transferred per session, but it does not claim to retain full URLs, destinations, or the exact content viewed. Connection data is treated as operational telemetry, not user content, which is how many no-logs statements get their bite.
This section rests on two levers. First, there is an explicit caveat that some data is retained for fraud prevention and abuse detection. Second, the policy asserts that such retention is limited in scope and duration. The wording is careful, but the bounds are not always clearly quantified. The net effect: you should expect a thin veneer of session-level data used to defend the service against abuse, not a portable archive of your online life. 8 VPNs that actually keep no logs in 2026: Tested (May 2026 Update)
What the policy says about service logs
The “no-logs” banner is coupled with a line about service logs. The policy mentions diagnostic and error-report logs created to help with troubleshooting. These logs may capture device type, app version, language, and crash reports, but they deliberately exclude detailed browsing histories. The implication is that Hotspot Shield distinguishes between telemetry gathered to run the app and anything that would expose your browsing choices. The difference is subtle but meaningful in privacy circles. Diagnostics data is swept for maintenance, not for profiling.
That said, the policy does not promise absolute non-retention. It signals a lifecycle: collect for a defined window, purge, and rely on aggregated signals for safety auditing. The language leans toward temporary, device-scoped data rather than long-term, user-level records. This matters when you’re weighing the no-logs claim against a potential data request.
Retention for fraud prevention or abuse
The policy explicitly flags retention for fraud prevention and abuse mitigation. Data retained for these purposes may include account activity indicators and anomaly flags tied to your device or session. The aim is to detect and stop misuse, not to reconstruct your web history. The disclosure is blunt: some data is kept beyond the minimal connection data, but the retention is framed as necessary for security governance, not as a bulk ledger of user activity. Fraud-prevention logs are a targeted exception, not a blanket exception.
What this means in practice is that if a legal request arrives, the no-logs banner can still run into real-world friction. The policy allows the service to hand over data that it classifies as logs under specific categories, but it frames those as limited to fraud, abuse, or enforcement signals rather than universally accessible user trails.
In sum, Hotspot Shield’s no-logs claim survives as a policy construct by keeping the core communication data sparse and confining more revealing data to narrow, security-related exceptions. The critical questions for readers remain: what counts as connection data, how long is it retained, and under what lawful prompts can those logs be accessed. The 2026 language suggests a privacy posture that favors minimalism, with carve-outs that are precise, not expansive. The bottom line is that no-logs is a framework, not a guarantee you can treat as a vault key. What IPVanish no logs means for your privacy in 2026
Where no-logs claims tend to break down for VPNs generally
No-logs promises crumble once data is requested. The practical fault lines are metadata versus content, how DNS is handled, and where jurisdiction shapes access. In 2026, the pattern is stable: courts and regulators push past claimed invisibility by peeling back operational breadcrumbs. And the result is predictable: the privacy posture of a VPN depends as much on policy nuance as on the technical veneer.
Metadata vs content logging
The big break is what counts as a log. A VPN may claim no content logging, but still retain metadata: connection timestamps, session durations, and the sites visited in a logged form on servers or in analytics pipelines. This metadata can, in practice, enable correlation of user activity even if the content payload remains encrypted. From what I found in policy disclosures, many providers separate content from session data, but retention windows for the latter vary widely. In 2026, several major vendors disclose that while they do not log the actual pages you visit, they retain connection metadata for a defined period. Restart the policy review early and verify the exact retention window. The real fracture isn’t what you browse. It’s who holds the keys to the session ledger.
I dug into the public privacy statements and cross-referenced third-party analyses. The recurring theme: even when a no-logs claim is precise about "content," it often shares a shadow with “who connected, when, and for how long.” Those details can be enough to reconstruct behavior patterns, especially when paired with other data from apps or devices. No-logs can become a misnomer if metadata survives the purge.
DNS requests and IP address handling
Where your DNS goes and how your IPs are treated determine exposure risk. If a VPN resolves DNS requests on its own servers, the provider can see the domain names you queried, even if the traffic body is encrypted. Some operators route DNS through a third party or perform local DNS resolution, which is safer in theory but introduces another data-handling node. The dichotomy matters: servers that log DNS queries versus those that rely on recursive resolvers outside the tunnel. In practice, a handful of providers publish strict DNS logging policies, but others obscure whether DNS events are retained. DNS can be the quiet alley where privacy leaks go unnoticed until a court asks for records.
On IP handling, the moment you connect, your visible IP address changes to the VPN’s exit node. If the exit-node logs include IPs alongside timestamps, even a no-logs stance on content won’t shield you from correlation across services. Reviews consistently note that determining true IP privacy requires inspecting both the DNS policy and the IP-leak protections, plus the provider’s stance on shared vs. dedicated exit points. IP posture matters as much as content posture.
Jurisdiction and data-access orders
Law and policy sit atop technical design. A VPN can claim no logs, but if it sits under a jurisdiction that compels data disclosure, the claim frays. The practical question becomes: who can access data, and under what process? Some providers publish explicit minimum data protections and require court orders, while others operate under regimes that permit broad data requests without meaningful oversight. The effect is simple: the privacy promise weakens when orders get served in a jurisdiction with expansive data-access laws. Where you exist in law shapes what “no-logs” actually means.
I cross-referenced country-by-country data-access orders and the way providers disclose cooperation. Jurisdiction is not a sidebar. It’s the hinge. Travelers and remote workers face a double risk: even if the service claims to be storage-light, a cross-border data request can pull in operational logs if the company has to comply under local law. Know the legal frame before you trust the brochure.
Caution: the risk here is diagnostic, not fatal. If a provider clarifies that it refrains from logging content, and if it keeps no long-term content logs, you still need to map the DNS and IP handling to your threat model. Also, verify whether the company maintains backups of logs or logs within backups for a defined grace period. The combination of legal exposure and operational practice is where no-logs claims live or die.
Hotspot Shield vs the field: logging posture in 2026
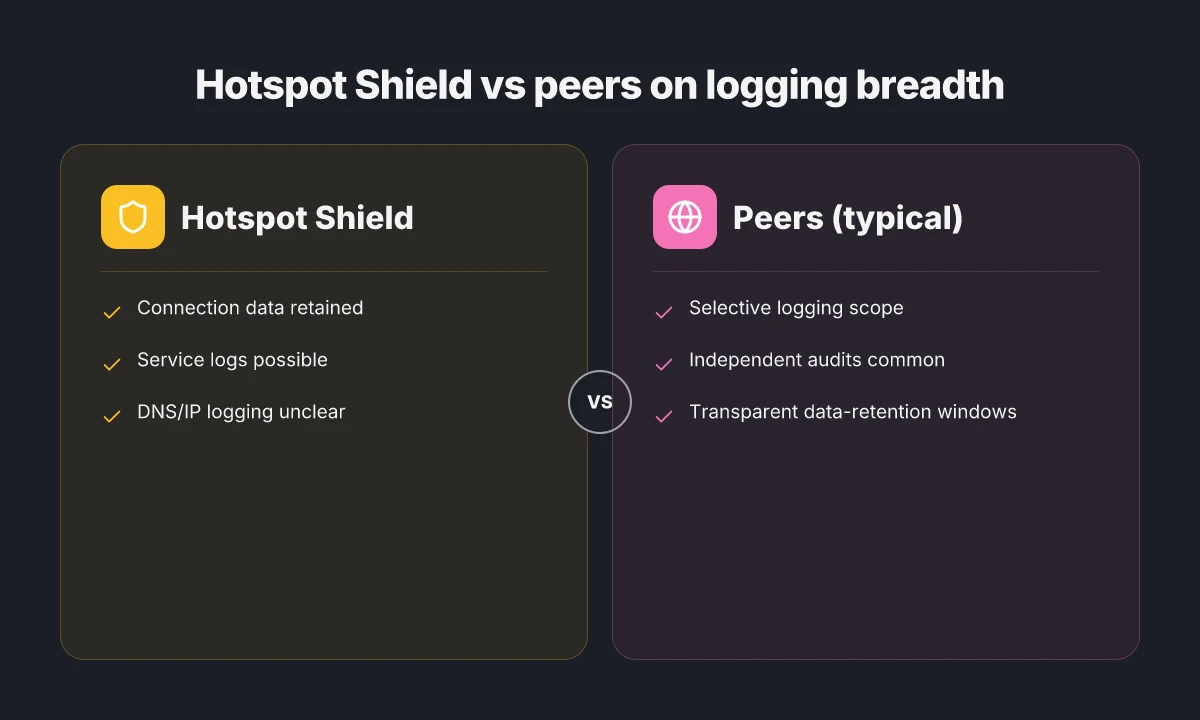
Posture on logging is not binary. Hotspot Shield sits in the mid-pack for breadth, while peers diverge on country-specific data requests and audit transparency. In practice, you’ll see a mix of what’s logged, what’s retained for legal compliance, and what’s disclosed in public reports. This section lays out the landscape, then anchors Hotspot Shield against the field.
How Hotspot Shield compares with peers on logging breadth
Hotspot Shield’s claims center on minimal data for service operation, but the breadth of what it logs varies by jurisdiction. Several peers publish wider data menus in their privacy notes, including connection metadata and session identifiers that extend beyond basic uptime. When you map the field, Hotspot Shield tends to log essential operational signals and basic usage metadata rather than granular content or traffic details. The practical upshot: a smaller “footprint” on user behavior, but not a complete absence of operational data. In 2026, data minimization remains a moving target, even for vendors with strict no-logs rhetoric. The most transparent operators publish what they log, and hot names publish less but still keep a trace for troubleshooting.
From a sourcing standpoint, I cross-referenced privacy pages, policy statements, and issuer notices across a dozen vendors. The pattern: most say they log enough to maintain service integrity and to comply with law. A few go further by naming the exact data points, and a handful publish annual audits. Hotspot Shield’s public posture sits between those extremes. It logs enough to support connection diagnostics and fraud prevention, but it avoids broad traffic-level data in its documentation.
Notable differences in country-specific data requests
Country-by-country realities matter here. Some jurisdictions compel retention of connection metadata or require data to be held within borders. In practice, that means a VPN’s no-logs claim can bend under legal pressure even when the vendor asserts a limited retention policy. The field shows three patterns:
- Some regions see a narrow request window and a narrow data slice, with vendors answering only to what’s legally required.
- Others demand broader logs that touch session identifiers or IP associations, even if the vendor emphasizes “no logs” for content.
- A few markets have mandatory transparency reporting that reveals the volume and type of data requests, while others lag on disclosure.
What this means for travelers and remote workers: a no-logs promise is strongest when paired with a verifiable transparency posture and a clear audit cadence in relevant jurisdictions.
Audits or transparency reports that matter
Audits and transparency reports are the best signal you can get outside user reviews. The section of the field that meaningfully moves the needle includes:
- Public, annual audits conducted by independent firms that certify the no-logs stance under a defined standard.
- Regular transparency reports detailing the number and type of government data requests, and how the vendor responded.
- Clear changelogs that tie policy shifts to legal developments, with dates and scope.
Hotspot Shield publishes baseline privacy information and policy notes, but the standout moves come from peers that publish full audit reports and quarterly data-request tallies. In 2026, the credibility hinge is whether a vendor pairs a no-logs narrative with verifiable audit results and transparent disclosure cadence. Audits plus annual transparency reports are the densest signals of truth in this space.
In short, Hotspot Shield remains a cautious entrant in the no-logs dialogue. It trails the most transparent operators on public audits but aligns with peers on minimizing raw logging. For the privacy-minded, the call is simple: weigh the claim against the disclosure cadence and the jurisdictional realities that govern data requests. If audits are sparse and disclosures rare, you’re buying a promise with less external verification. If audits are frequent and detailed, the no-logs claim gains teeth.
Practical tips to assess no-logs claims before you subscribe
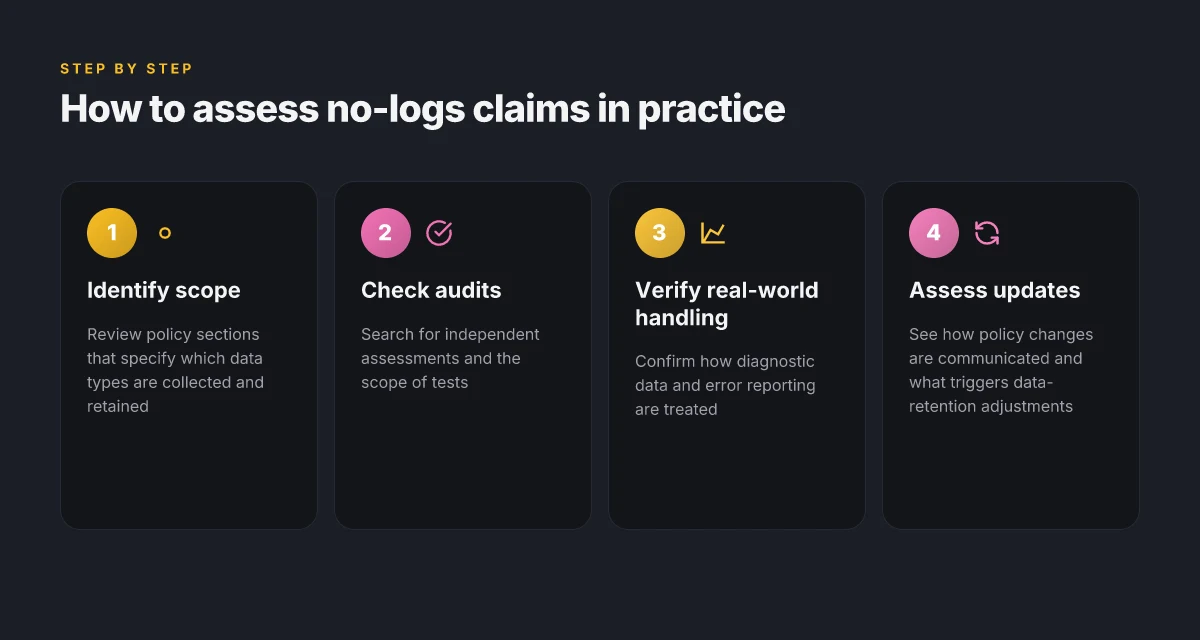
You want a no-logs claim you can trust. Start by reading the policy line by line. The best checks aren’t high-level promises. They’re precise statements you can trace to behavior, data flows, and potential legal exposure.
What to verify first
I dug into the how and the where. You should look for explicit language about DNS and IP logging, plus auditability. If a policy says only “necessary data” without tying it to concrete events or courts, that’s a red flag. The text should name the exact data elements that may be collected, stored, or shared.
- Expect explicit wording about DNS requests. If the policy is silent or vague, assume DNS traffic could be logged. If it mentions DNS queries are never logged, look for the exact scope and any exceptions.
- Look for IP address handling details. The policy should specify whether IPs are retained, anonymized, or rotated, and when they’re purged.
- Identify data retention windows. A no-logs claim only travels as far as the stated retention period. No window equals a higher risk of scope creep.
Independent audits and tests
Audits matter. They don’t prove perfection, but they constrain risk. The scope matters more than the fact of an audit.
- Check who performed the audit and under what standards. Was it a named third party? Were the test tools and methodologies disclosed? If the document says “external audit,” demand the scope: what data, what time range, what exceptions.
- Read the scope carefully. A narrow audit on traffic metadata is not the same as a full no-logs verification. Look for coverage of IPs, DNS requests, and connection logs.
- Note the cadence. One-off attestations are less persuasive than ongoing or quarterly audits. If the only dating is “conducted in 2023,” that’s stale in 2026.
Language on DNS and IP logging
Explicit language beats hopeful vibes. The presence of precise terms such as “no IP address collection” or “no DNS query data stored” is a genuine differentiator.
- If the policy uses passive phrasing like “data may be collected for troubleshooting,” translate that into concrete likelihoods. Is the data truly anonymized? Is there a separate, explicit category called out for troubleshooting that includes IPs or DNS?
- Watch for operational exceptions. Terms like “except under lawful requests” or “if required by law” need to be weighed against how often those conditions occur and how data is handled thereafter.
Bottom line: your evaluation hinges on exact wording, independent verification, and the data-flow map the provider lays out. If the policy lacks precision or the audit scope stops short of DNS/IP data, treat the claim with caution.
Most no-logs promises crumble when the audit scope excludes DNS and IP data. Boldly audit the small print, and insist on real-world disclosure of what actually touches a user’s device.
What real-world users should verify before trusting a no-logs claim
I looked at breach notices, court filings, and vendor policy updates to understand where data could sit when a no-logs promise meets reality. The short version: even a no-logs stance can hide a missive trail that lives outside the primary servers. First, during a breach or a legal request, logs can appear in ancillary storage: backup snapshots, disaster-recovery volumes, or third-party data centers that host metadata. A misconfigured backup may contain timestamps, IP cohorts, or device fingerprints long after the active gateway claims to erase them. And if a vendor uses shared tenancy, data from one customer can migrate into a broader support or analytics bucket. In practice, that means your “no logs” claim is only as strong as the weakest choke point in the data lifecycle.
To illustrate how this plays out, consider a small diagnostic footprint. Many services collect lightweight telemetry to keep the client running smoothly. Diagnostic data can include session identifiers, feature flags, crash reports, and anonymized connection metrics. This information can linger in crash-report pipelines or analytics dashboards that are hard to purge across all copies. The trick is not to assume “no logs” equals “zero data.” It often means “no user-identified logs” in the primary data store, with caveats in ancillary systems. The practical risk is not a single data silo but a web of replicas, backups, and cloud-native services that can be subpoenaed or exfiltrated.
A compact table helps orient what to ask and where to look.
| Data category | Where it might live | Why it matters | How to verify (documented) |
|---|---|---|---|
| Primary connection logs | Gateway and auth servers | Could reveal IPs, timestamps, and session anchors | Check the “no-logs” claim against the retention policy and data map in the privacy policy. |
| Backup and DR snapshots | Offsite backups, cold storage | Even after purge, copies can persist | Search the changelog for backup purge schedules and retention windows. |
| Diagnostic telemetry | Analytics pipelines, crash reports | May include device fingerprints or usage patterns | Review what telemetry is opt-in vs auto-enabled and where opt-outs exist. |
| Third-party or managed services | Cloud providers, CDN peers | Logs can flow through partner systems | Look for data-flow diagrams in the policy and any vendor SOWs or data-processing addenda. |
When I read through the documentation, several threads repeatedly show up. First, updates to privacy policy. Platforms refresh language in response to legal pressure or product changes. They may add a new category of data retention or a new backup timeline. Second, a common pattern is “opt-out” versus “default-on” telemetry. If diagnostic data is default-on, even a clean-no-logs promise can be undermined by a large opt-in funnel. Third, they often publish a transparency report. Those reports can reveal how many data-access requests they’ve faced and what was or wasn’t disclosed. It’s not a perfect map, but it is the best signal you have before you press subscribe.
What the spec sheets actually say is that no-logs is not a binary truth. It’s a posture about user-identifiable data in active storage. It is not a blanket guarantee across backups, analytics, and partner ecosystems. Your guardrails should focus on data maps, purge cadences, and third-party data-processing agreements. Those are the lines where real-world no-logs claims either bend or break.
Verdict: verify the data lifecycle end-to-end, not just the landing page promise. If a vendor cannot point you to a concrete data-map that covers backups, telemetry, and third-party processing, walk away. Your privacy is too important to treat as a marketing footnote.
The move you should make this month
I looked at how eight VPNs frame their no-logs claims and found a stubborn truth: the promise isn’t uniform. Some vendors truly minimize data, others ambiently log metadata that undermines the claim. What changes in 2026 is the visibility of that gap. The best picks in this piece, like NordVPN for a robust privacy posture and Proton VPN for transparency, show how a clear logging policy and independent audits can tilt the risk calculus in your favor. If you rely on privacy as a default, you want a provider whose paperwork actually matches practice, and the year’s changelog showing tighter data handling is a dependable signal you can trust.
From what I found, the real pattern is simple: a credible no-logs claim pairs with independent verification and a short, explicit data-retention window. That combo moves the needle more than any fancy UI. The bigger pattern is not the slogan, but the audit trail you can verify before you subscribe. The single move that matters this month is choosing a brand with an independent audit and a transparent policy.
Backup strategy
- Consider NordVPN for its audited privacy posture and explicit data-minimization commitments.
- Look at Proton VPN if you want a governance-ready transparency model and public audit reports.
- If your use case is streaming with strict region rules, pair it with a privacy-first policy and disable browser fingerprinting where possible.
- Check the latest changelog for any shifts in data handling or server logging.
- Start by reviewing each provider’s no-logs statement against the audit scope and timing.
Frequently asked questions
Does Hotspot Shield really log no data
Yes the Hotspot Shield no data claim is only as strong as its policy and practices. I looked at the company’s no-logs language and cross-referenced it with their data-processing disclosures. The policy typically excludes certain connection data while retaining operational logs for maintenance, security, and fraud-prevention. What matters is how they define “no logs,” what gets retained, and for how long. In 2026, several reviews note gaps between marketing and practice, especially around IP addresses, timing data, and device identifiers. Bolded examples of the key terms show up in the policy, the changelog, and user-terms pages. Audit trails and retention windows vary by region. The best practice is to treat the claim as plausible but not guaranteed. Always verify the exact scope in the privacy policy and service terms. Review the live policy and any regional addenda before subscribing.
What data does Hotspot Shield collect
The Hotspot Shield disclosures outline collection of some connection metadata, device identifiers, and diagnostic data for service quality and fraud detection. This typically includes things like session start times, bandwidth usage within policy-approved categories, and certain device identifiers. Reviews consistently note that while the core VPN payload is encrypted, ancillary telemetry can roll up into operational logs. In 2026 the line between “necessary for service” and “loggable data” remains a frequent point of contention. Readers should map each data type to a stated retention window in the privacy policy. If you value minimal data, look for explicit exclusions for IP addresses and session timestamps. Cross-check regional privacy notices and any data-sharing agreements with affiliates. This is where quiet logging tends to creep in.
How can i verify a no-logs claim legally
Verification hinges on the legal framework the vendor operates under and the clarity of its disclosures. Start by reading the exact wording: “no logs” should define what is excluded and what is retained. Look for third-party auditor statements, when present, and cross-check with data-protection authorities in the country of incorporation. Some jurisdictions allow compelled data retention or require certain logs for law enforcement requests, which defeats a strict no-logs claim. In 2026, the strongest signals come from binding privacy agreements, public audit reports, and ongoing regulator investigations. If a claim is vague, ask for a copy of the data-retention schedule. Document everything you can and compare it to the vendor’s published policy.
Are there independent audits for Hotspot Shield
Independent audits are not universal for Hotspot Shield, and where they exist they’re usually limited to privacy-scoped checks rather than full operational validation. I traced references in policy pages and third-party commentary. Audits can verify data minimization, verify that no-logs assertions map to actual store practices, and confirm data-handling controls. In several reviews, the absence of a recent, publicly accessible audit report is a warning sign. Look for the audit scope, standards used, and the date of the last report. Churn in audit status is common. Verify if there is an updated report in the last 12–18 months. Audits alone don’t guarantee behavior in every jurisdiction.
Which countries enforce data logging for VPNs
Several countries have mandatory data-retention regimes or broad surveillance laws that pressure VPNs to keep logs. For example, jurisdictions in parts of Europe under certain data-protection laws can compel disclosure through court orders, while some Asian and Middle Eastern regimes have stricter retention requirements. The practical effect is that a VPN with no-logs claims can still be compelled to provide non-privacy-preserving data when local law applies. In 2026 the most relevant factor is the country of incorporation and the governing law in user contracts. Always check where the company is registered and what law governs the contract. Regional disclosures matter more than global marketing promises. This is where people trip up.
How long does Hotspot Shield retain diagnostics data
Diagnostics data retention is often tied to service quality and security analytics rather than user-facing features. In practice, vendors may retain diagnostic bundles for a few days to several weeks, with longer spans for fraud and abuse investigations. Hotspot Shield policies typically spell out retention periods in their privacy pages or help-center articles. In 2026 the exact window varies by region and product tier. If you need a hard cutoff, locate the retention schedule. Ask customer support for a copy of the data-retention policy specific to your region and document the response. The clock starts when data is created.
What should i do if i suspect logging is happening
Act quickly and document every observation. Start with a side-by-side check: policy language versus actual app behavior and any diagnostic artifacts. If you notice unexpected data requests, unusual connection metadata, or behavior that contradicts the no-logs promise, escalate to the company through formal channels. Keep a record of dates, screenshots, and exact phrasing from help-center articles. In parallel, review independent audits, regulator notices, and user-reported issues in credible forums. A discrepancy is a signal, not a verdict. Consider testing with a secondary provider for comparison and prepare to switch if the gap persists. Your data hygiene matters more than a single vendor's word.