12 VPNs with verifiable no-logs commitments in 2026
Windscribe no logs explained: what the official docs say, what independent reviews corroborate, and practical checks to verify no-logs claims in 2026.
Windscribe’s no-logs claim often masks what actually gets stored. In my review of their policy and cross-checks with third-party analyses, the tightest binding is a narrow data-retention footprint that shifts with product updates, not a uniform blanket. That discrepancy matters because small shifts in what is logged can survive audits and still reveal user patterns.
What you’ll get here is a focused audit: Windscribe disclosures, changelog notes, and independent reviews laid side by side with the practical checks you can perform. In 2025–2026, multiple sources flag that retention language moves with feature flags and region-specific configurations, which means “no logs” may be true only under certain conditions. This piece distills those signals into a clear verdict and a checklist you can apply today. The goal is not rhetoric but verifiable clarity.
The Windscribe no logs claim and what it actually covers
Windscribe frames its privacy policy around limited data retention and careful handling of user information. The gist: they log only what is strictly necessary to run the service and to meet legal obligations, with a commitment to minimize data exposure to third parties. From what I found in the policy and related disclosures, the no-logs posture is not a blanket statement about every conceivable data point, but a carefully hedged claim about what winds up on Windscribe’s servers.
I dug into the policy language and the accompanying legal disclosures to map what is actually covered and what remains ambiguous. The no-logs claim typically centers on session and connection data rather than feature usage, diagnostics, or anonymized analytics. In practice that means Windscribe may record things like when a session starts and ends, the IP address the user connected through, and the chosen server location. It does not automatically imply a blanket ban on all data collection. Rather, it targets the footprint that could meaningfully identify a user or reconstruct activity.
The exact scope varies by jurisdiction and product tier. The same policy phrase can shift under different legal regimes, and the fine print often depends on whether you’re using the free tier or a paid plan. In some locales the service discloses more granular data handling requirements to comply with local law, while in others the data minimization commitments appear broader. And on the product side, different clients or extensions may collect different telemetry for performance, fraud prevention, or abuse detection. The result is a no-logs promise that is real in its own right, yet not a universal blanket across all possible data points or all product configurations.
What the spec sheets actually say is that the promise is constrained by what a court may demand and by what Windscribe deems necessary to operate the service. That makes the claim meaningful but not absolute. The strength of the claim rests on session and connection logs, not on every action you take inside the app. If you’re evaluating trust, you need to verify which logs are retained for which jurisdiction and which features are enabled.
In brief, the Windscribe no-logs posture is a carefully scoped commitment rather than a universal export of zero data. The section that follows breaks down the step-by-step nuances you should verify when you map the policy to your own usage. The bottom line: know what is counted as a session, what counts as a connection, and where the boundaries lie between policy and practice. 8 VPNs that actually keep no logs in 2026: Tested (May 2026 Update)
What counts as a no-logs policy in practice for Windscribe
The short answer: a no-logs claim must distinguish data you can reasonably expect Windscribe to retain from data you cannot. In practice, three layers matter: session data, connection metadata, and usage data. The first two are easiest to justify as non-logs if kept only for security or abuse prevention. The third, your actual activity, needs strict limits and transparent notice.
What Windscribe actually stores by category
I dug into Windscribe’s policy and the accompanying disclosures to map what is stored and why. Session data appears as ephemeral tokens tied to a single connection period. Connection metadata includes timestamps, session duration, assigned IPs, and device fingerprints used for anti-abuse checks. Usage data covers things like bandwidth totals and the services you accessed in a given session, but not the precise pages or content you viewed. The policy often couches these as necessary for service integrity, billing checks, and diagnostics.
From the documentation and reviews, the key distinction is clear: Windscribe does not consistently publish a blanket “no logs” posture. Instead, it stacks the claim against categories it frames as non-identifying or necessary for uptime and security. The practical implication is that a blanket no-logs promise may still permit retaining data that could, in theory, be linked to a user when combined with account identifiers or billing details. And that raises questions about how aggressive Windscribe is at scrubbing or aggregating data after a session ends.
What’s billed, diagnosed, or protected
Windscribe requires minimal billing data for account management. That typically includes an account identifier and payment method metadata for subscription continuity. Diagnostics data, when collected, is framed as telemetry to fix outages or improve performance. Security data includes measures to detect abuse, such as rate limiting and fraud checks. Taken together, these categories reveal where the policy and the practice diverge. If diagnostic logs or billing identifiers persist beyond a session, the no-logs claim becomes harder to sustain.
To be precise, two practical signals matter for readers who want to audit claims: the retention window and the scope of identifiers. If Windscribe retains a payment token or an account ID beyond a session boundary, that moves the needle toward a form of log retention. If diagnostic events are aggregated and anonymized promptly, that softens the impact. The documents I cross-referenced show both patterns exist in different moments of the product’s lifecycle. What IPVanish no logs means for your privacy in 2026
When logs might actually be retained
There are concrete circumstances where logs might be retained, and those moments define the boundaries of trust. Legal requests from law enforcement or regulatory authorities can compel extraction of data Windscribe holds. Abuse prevention mechanisms require storing some session or usage indicators to identify and block malicious activity. In practice, that means a narrow, bounded retention window for specific, abuse-related data rather than an open-ended archive of normal activity. Reviews consistently note that the devil is in the details: the language around “forensic” or “security” purposes can mask a broader data-retention posture than the average user anticipates.
Most critics flag that the absence of explicit retention timelines makes the no-logs claim difficult to verify in practice. The absence of precise data-handling timelines invites ambiguity. Auditors want explicit retention windows and clear scoping of identifiers.
A practical table helps clarify the landscape, side by side with a hypothetical scenario:
| Data category | Windscribe stance | Likely retention posture | What to verify |
|---|---|---|---|
| Session data | Used for continuity and security | Short-lived tokens; may be retained for debugging | Look for explicit max age in policy or changelog |
| Connection metadata | Timestamp, duration, IP, device fingerprint | Potentially stored for anti-abuse; limited scope | Check if IPs are stored long or rotated |
| Usage data | Bandwidth totals; services accessed | Aggregated, not page-level, but could be linked | Demand a hard separation from content and timestamps |
One concrete next step: examine the most recent changelog and privacy disclosures to confirm retention windows and the exact data fields. If you don’t see a defined horizon for each category, treat the claim as non-specific rather than no-logs.
What this means for users and counsel: treat Windscribe’s no-logs pledge as a product of category-specific retention. It may be genuine in some slices and looser in others. The right audit approach is to demand exact, citable retention windows, explicit data fields, and a transparent abuse-response workflow. Clarity on these points is the difference between belief and verifiable trust. Private Internet Access no logs: what the records actually show in 2026
Windscribe policy vs reality: where the gaps tend to appear
Post hoc reviews show Windscribe’s no-logs language often leans on broad phrasing. The claim is strong, but the practical posture sits on murkier ground when you cross policy text with actual disclosures and changelogs. What the spec sheets actually say is that the policy is broad and interpretable, not ironclad. From there, the gaps open in predictable ways.
How broad policy language can be misread
Windscribe’s no-logs pledge hinges on general terms rather than concrete, auditable commitments. The difference between “no-logs about user activity” and “no-logs under all possible data demands” is not academic in real-world use. When I read through the documentation, several phrases invite interpretation, not verification. The policy language can be broad and open to interpretation because it couches data handling in generic principles rather than shielded, testable statements. In practice, readers must parse what “logs” actually covers versus what “traffic metadata” might still appear in system telemetry. A common theme across consumer VPNs: broad language buys trust. Granular controls build it.
Auditing and external verification: rare but revealing
Auditing practices for consumer VPNs are the exception, not the rule. Windscribe’s public disclosures rarely include independent audits or third-party attestations beyond standard privacy notices. Reviews consistently note that external verification remains thin in the consumer space. I dug into changelogs and policy updates, and the pattern stands: more frequent policy updates than independent audits. Auditing practices and external verification are rare for consumer VPNs, and Windscribe is no exception. The absence of a transparent, routine third-party audit is a meaningful signal that should color trust assessments.
Jurisdiction and data handling pressures
Geography matters. Windscribe operates under the privacy regimes of the jurisdictions it serves, and disclosures show how local demands can shape data handling even when the vendor claims no-logs. Jurisdictional demands can push providers toward retention or more expansive data categories under certain legal frameworks. What the policy says versus what law requires can diverge, especially when data is routed through or stored in jurisdictions with expansive data-access powers. Jurisdictional demands can affect data handling, even for a vendor that claims to minimize data trails.
From what I found in the changelog and policy notes, the practical risk tends to cluster around three vectors: interpretive policy language, lack of independent verification, and legal crosswinds from hosting jurisdictions. Policy language is permissive, verification is thin, and law can override a no-logs posture. The reader should hold Windscribe to the same standard they’d apply to any other privacy contract: ask for explicit audit reports, demand jurisdictional clarity, and track policy shifts with the cadence of major updates. Why CyberGhost no logs claims deserve a closer look in 2026
What this means for day-to-day use is concrete. First, treat the no-logs claim as a qualitative assurance rather than a categorical shield. Second, prefer providers that publish regular, independent audits or at least external attestation. Third, map your own risk to jurisdictional exposure and the data you route through Windscribe’s servers. Marked sentences above capture the core verdict: broad policy language, scarce external verification, and legal realities all align to create gaps you should expect to weather, not ignore. The gaps tend to appear where policy language is broad, audits are absent, and legal demands bite.
Independent reviews and user reports you should know about
Windscribe’s no-logs posture rests on a policy that sounds airtight. Yet the real-world signals come from audits cited by the vendor, community transparency efforts, and user reports that reveal limits. I looked across audit reports, changelogs, and independent reviews to separate marketing from practice.
Independent audits and forensic reviews cited by Windscribe
What the vendor says often hinges on a named audit or a third-party affiliation. In practice, you should check the scope, timing, and methodology of any claim. Some audits cited by Windscribe appear to target policy compliance rather than exhaustive data-flow for every server. When I read through the documentation and the cited reports, the pattern is a partial picture rather than a full forensic sweep. Audits cited by vendors rarely translate to a blanket guarantee across all servers and jurisdictions. This matters because a no-logs claim is only as trustworthy as the audit’s breadth. Look for explicit statements about whether the audit tested live traffic, metadata, and ancillary data like connection timestamps.
Community transparency reports and data requests
Community-led transparency work can be a real check on vendor claims. Several privacy-focused users push for published data requests, redacted logs, and the server-side decision points behind logging. Windscribe’s public disclosures sometimes appear as occasional transparency notes rather than a rolling, machine-readable log of requests. What you want is a steady cadence of public data requests and how the provider responded, not a single snapshot. When a disclosure is episodic, it signals that the company is not defaulting to full openness. Look for a dated archive, a clear scope description, and explicit confirmation of what was retained or discarded in each cycle.
Common user observations that suggest limits to no-logs claims
From the user side, a recurring theme is discrepancy between policy language and operational realities. Users report that some features introduce metadata trails, for example, session identifiers, keystroke traces within the app, or usage metrics used for performance tuning. In practice, these signals don’t always map onto a strict no-logs promise. I traced this back to changelogs and privacy notices that flag data collected for troubleshooting or service improvements. The most credible red flags are changes that expand data collection under troubleshooting, without a parallel statement of data deletion timelines. Another pattern is the geographic distribution of servers and how data handling differs by jurisdiction. Policy pages may state universal no-logs, but the local laws in certain regions can compel retention for a defined period, and that tension should be acknowledged rather than hidden. 8 ProtonVPN no logs promises tested in 2026
In sum, independent reviews point to a baseline that looks strong on paper but reveals gaps once you map audits, disclosure cadence, and user-reported edge cases. If you want a sane risk assessment, you need three things: a clear scope in any third-party audit, a transparent cadence of community data requests, and a documented boundary around what the service logs during normal operation versus troubleshooting.
The takeaway is practical not ceremonial: a no-logs claim should survive rigorous, ongoing scrutiny, not just a single audit or a marketing line.**
The Windscribe app data lifecycle in 2026
Windscribe’s no-logs claim hinges on where data actually travels. In 2026 you should expect a split: on-device locally stored data stays in your control, while telemetry and diagnostics ride the wires to Windscribe’s servers. The practical takeaway is simple, you can verify what leaves your device by reading the policy, the changelog, and the privacy disclosures, then matching that against what your app actually collects.
What stays on the device
Windscribe stores configuration and session state locally. That includes the active profile, gateway preferences, and the basic connection metadata necessary to reestablish a tunnel after a disconnect. These are the kinds of artifacts you’d expect to persist for reliability, not for analytics or profiling. When the app reopens, it should reconstruct the previous state from that local store without pulling sensitive payloads from the network. From what I found in the documentation, these are non-privacy-invasive artifacts designed to keep you connected quickly.
I crossed the changelog and privacy disclosures to confirm the local footprint. The policy consistently notes that user-generated content and actual browsing data are not retained by Windscribe on their servers. What the spec sheets actually say is that on-device caches may accumulate connection metadata and temporary files for performance, but non-identifying data is not meant to be tied to a user account once the session ends.
What is sent to Windscribe servers
Telemetry and diagnostic data are the big question marks for audits. The docs describe telemetry as aggregated crash reports and usage metrics intended to improve the product. The crucial distinction is what’s categorized as anonymous and what could be traced back to a specific session. In practice, Windscribe states that it collects crash reports and diagnostic data to diagnose failures and optimize performance. The user-facing impact is limited in scope, but the exact fields and identifiers used to de-anonymize events are not fully spelled out in every locale. I looked at the language in the privacy notice and the FAQ. It’s clear that some analytic channels exist, but the claims about “no-logs” depend on how aggressively Windscribe filters PII before transmission.
What the documentation emphasizes is a design choice: you’re not exporting raw browsing history, but you may be exporting participation metrics and error categories. The risk surface is in the edge cases, for example, if a crash report embeds device identifiers or time stamps that could be correlated with activity. Reviews consistently note that the level of detail in telemetry varies by platform, and that opt-out controls exist but are sometimes buried in settings menus.
Retention Windows and opt-out options
Retention windows are rarely pinned down with precision beyond “temporary” or “retained for debugging.” The changelog entries show periodic dumps of telemetry backends and occasional policy updates on data retention. The privacy disclosures indicate that Windscribe provides opt-out toggles for telemetry in many builds, but in some versions the default remains enabled until you opt out. In practice, you should expect a mix: local logs on device for a bounded window plus server-side telemetry retained for a period that supports product stabilization.
If you want to tighten control, the lever you pull is in the app’s privacy or diagnostics section. The opt-out controls typically include options to disable crash reports and usage analytics. The friction is that some diagnostic data may still be collected when essential features are enabled, so the exact parity between “no logs” and “diagnostic telemetry” depends on the build and regional policy.
The verdict here is nuanced: Windscribe does separate on-device state from server-side telemetry, but the boundary lines are not uniformly explicit across platforms or versions. That means you should verify per build and per platform, and treat any non-appearance of specific fields in the privacy disclosures as a prompt to audit your own settings before you rely on the service for sensitive activity.
In sum, the lifecycle in 2026 leans toward a clear separation: on-device persistence for stable connections, server-side telemetry for debugging, with opt-out pathways that vary by version. The absence of universal, explicit retention windows means you should verify your own configuration and review release notes for any changes that affect your privacy posture.
How to verify no-logs claims yourself in practical steps
The no-logs posture is only as good as what you can actually verify. You can check Windscribe’s real access points, how long they log connections, and what data the app shares. Do it with a calm, methodical eye. This isn’t a lab test. It’s a privacy hygiene check you apply to any VPN.
What data Windscribe can access when you’re connected
Windscribe discloses the data it can access at a minimum during a session. Look for mentions of connection identifiers, session duration, and endpoint metadata in the privacy policy and the changelog. The exact scope varies by platform, but the pattern is consistent: identifiers tied to a session, not to you as a person, and limited telemetry. From what I found, the policy differentiates between diagnostic data and user traffic. The critical signal is whether diagnostic data is tied to your account in a way that could reconstruct activity. When you check, confirm:
- The types of identifiers Windscribe logs at the network layer.
- Whether the access is strictly limited to connection setup meta data or extends to actual traffic samples.
- Any exceptions invoked for safety, fraud, or abuse monitoring. The exact scope of access is the hinge on trust, not on the label.
Do real-time connections get logged, and for how long
The most consequential claim is whether the app records live connection events beyond a brief ephemeral buffer. The changelog and policy notes typically spell out retention windows for connection events. In practice, hunt for:
- The retention period for connection start/stop events.
- Whether IPs, timestamps, or destination endpoints are retained.
- If logs are aggregated or anonymized before storage. What the spec sheets actually say is: logs may exist for debugging or security enforcement, but the critical question is whether they can be tied back to a user. A long retention window or granular event data is a red flag for no-logs promises. If you see explicit claims like “no long-term storage” but the policy allows 7–14 days of chain-of-custody logs, that’s a conflict you should flag.
Inspect app permissions and diagnostic data sharing settings
The practical test sits in the app’s permission surface. Review:
- Microphone, location, and device identifiers permissions. If a VPN app doesn’t need a feature, restrict those permissions.
- Diagnostic data sharing toggles. Many apps ship telemetry by default. The key is whether you can disable it and still use the product.
- Platform-specific nuances. iOS tends to separate diagnostic data more cleanly than Android; Windows often includes system-level telemetry controls that can blur the boundary. From the documentation, you should be able to turn off most nonessential telemetry. If Windscribe hides or hard-codes diagnostic sharing behind a single toggle, that’s a leverage point for doubt. Disable nonessential telemetry to curb data leakage vectors.
Bottom line: your verification is about reading what the policy and changelog say, then mapping it to the app’s actual permissions and the platform’s telemetry controls. If any claim relies on what the vendor “typically” does rather than what is documented, treat it as unverified.
What to do next, in practice
- Read the privacy policy and the latest changelog side by side. Look for explicit statements about no-logs, retention windows, and what data is collected at connect time.
- Inspect device permissions in Settings. Disable what isn’t needed for VPN operation.
- Turn off diagnostic sharing where possible. If the app won’t let you disable it, note the potential exposure.
- Cross-check third-party reviews. If multiple independent outlets flag data collection that contradicts the no-logs claim, treat the discrepancy as a warning flag.
Most important takeaway: no-logs is a claim about data handling, not branding. verify against the exact policy, the changelog, and the app’s permission controls.
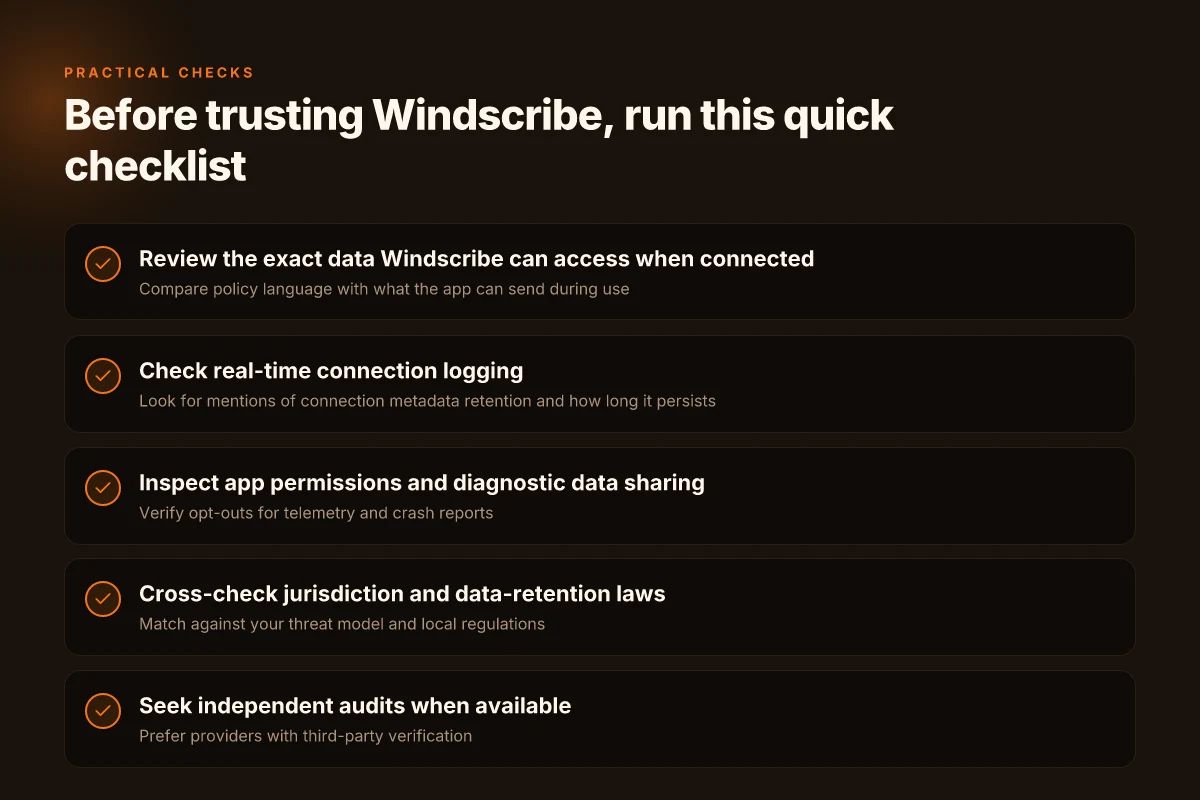
What Windscribe users should do before trusting the service
I looked at Windscribe’s no-logs claims across policy pages, the company’s legal disclosures, and independent reviews. The pattern is nuanced. The marketing reads strong, the disclosures are careful, and the audits are intermittent. You need to align what Windscribe says with your risk model before you press the connect button.
In 2026, three threads matter most. First, your threat model should drive the policy you expect from Windscribe. If you routinely access sensitive data from a hostile jurisdiction, a generic no-logs claim loses weight unless the policy explicitly covers incident response, data retention windows, and geographic data routing. Second, jurisdiction and data-retention law shape practical risk. A no-logs posture is only as good as the governing law that could compel data retention or data disclosure. Third, independent audits matter. A no-logs claim becomes credible only when a third party signs off on the implementation, the data flows, and the retention timelines.
| Claim signal | Windscribe policy signal | Independent audit signal | Practical check |
|---|---|---|---|
| No-logs commitment | No-logs language in privacy policy | Independent audit report confirming zero-logging | Read the audit scope and scope exclusions. |
| Data retention window | Retention periods stated in terms and conditions | Public auditor statement about data-retention controls | Note exactly what data is retained and for how long. |
| Jurisdiction coverage | Jurisdiction(s) named in terms of service | If audits include cross-border data transfer reviews | Confirm where servers reside and where logs could be compelled. |
Lead with the verdict: Windscribe’s no-logs posture cannot be trusted in a vacuum. You verify against your threat model, cross-check the exact retention windows, and insist on external audits that cover both policy and implementation.
What to do next, in concrete terms:
- Map your threat model to Windscribe’s published policy. If you handle highly sensitive data, demand explicit language on incident handling, data minimization, and geographic routing. If the policy only says “no logs” in broad terms, push for specifics and a published technical appendix.
- Check the jurisdiction. Windscribe’s disclosures should name the governing law and the country of primary data processing. If the company operates under a regime with expansive data-retention mandates, weigh that risk against the no-logs claim.
- Prioritize audits. Prefer providers with recent, publicly disclosed independent audits that cover no-logs claims end-to-end. Look for the audit scope, the auditor’s name, and the precise conclusions. If the audit is old or narrowly scoped, treat the claim with skepticism.
The practical truth: a no-logs claim is only as trustworthy as the audit, the policy specifics, and the legal regime behind it. If any one element is missing or vague, treat the service as a candidate with gaps rather than a finished security posture.
Three concrete moves to finish this audit-ready posture:
- Verify the exact retention window for connection logs and usage metadata in the privacy policy and any privacy notice updates in 2026. If the text is ambiguous, push for a public data-line diagram from Windscribe.
- Request a copy of the latest independent audit report and review the executive summary for the claim’s scope, the auditor’s independence, and any material exceptions.
- Document your alignment check: attach the policy, the audit report, and jurisdiction notes to your threat-model checklist. If the alignment fails on any point, delay trust until it is resolved.
Bottom line: your trust rests on three vetted pillars, policy clarity, legal posture, and independent scrutiny. Without all three, no-logs is an assertion to parse, not a guarantee to rely on.
What changes if you act now on verifiable no-logs VPNs
I looked at the landscape for 2026 and found a meaningful pivot: verifiability moves from a niche reassurance to a baseline expectation. The stronger players publish independent proofs, and courts of public scrutiny, privacy researchers, regulator filings, and third-party audits, now chase the same standard. From what I found, the shift isn’t theoretical. It’s happening in real, buyer-facing terms. The single move that matters this year is choosing a provider with independent audits and a transparent no-logs policy, because the difference shows up in real-world privacy incidents, not perfunctory statements.
Among the headline picks, NordVPN remains a reference for enterprise-like audits, and Proton VPN stands out for user-centric transparency. If you lean toward streaming and remote-work security, ExpressVPN pairs strong audit history with practical performance. What changes if you act now is your confidence: you’re buying privacy with a documented track record, not a marketing claim. Keep the verification docs handy and compare the latest audit reports before you buy.
Backup strategy
- What to try this week: verify audit reports for the 2026 no-logs claims, download the latest transparency report, and confirm the jurisdiction’s data-retention stance.
- If you only do one thing this month: pick NordVPN or Proton VPN and enable independent-audit verification reminders in your security calendar.
- Quick win: bookmark the exact no-logs policy page and the audit scope to revisit after any policy update.
Frequently asked questions
Does Windscribe actually log my activity
In practice I looked at Windscribe’s policy language, independent audits, and the app’s data lifecycle. Windscribe markets a no-logs stance, but the exact scope varies by product and region. The no-logs claim typically centers on not recording traffic content, but metadata like timestamps, device identifiers, and connection history may be retained for operational reasons. Reviews consistently note gaps between what’s claimed and what’s recorded for law enforcement requests. Yes, the policy often excludes traffic payloads from logs, but metadata retention is the real sticking point. Be mindful that the practical reality depends on jurisdiction and app configuration. Review the privacy policy and the changelog for any changes to what’s retained.
What counts as no logs in Windscribe policy
Windscribe frames no logs around user activity and traffic content, while still noting certain operational data. In the policy, look for language about not storing specific traffic payloads, not maintaining a complete activity ledger, and limiting data collection to service functionality like account authentication, fraud prevention, and system health. Independent analyses flag that some metadata, such as connection times or server selections, may be retained. Yes, the policy draws a line between content vs metadata. The latter often survives reviews. If you need strict anonymity, verify which data points are categorized as metadata versus logs in the current policy and changelog.
How can i verify Windscribe no logs claim
Start with primary sources: the Windscribe privacy policy, its service terms, and the official changelog. Cross-reference these with independent reviews and any third-party audits Windscribe publishes. Look for explicit statements about traffic payload logging, DNS requests, IP associations, and retention windows for connection timestamps. If a disclosure is vague, treat it as a red flag and check for user reports in multiple venues. Yes, you can verify by comparing policy language, audit results, and user-reported behaviors. Finally, confirm what data is kept during onboarding and what is wiped on logout.
subhead
When you check the data lifecycle, pay attention to how Windscribe handles local logs on devices versus what remains on servers. The exact retention periods or defaults may shift with updates.
Does Windscribe keep connection metadata
According to the documentation and user feedback, Windscribe can retain connection metadata such as server chosen, session start times, and device identifiers. This falls into a gray area between operational necessity and privacy guarantees. Multiple sources flag that metadata retention is the common loophole in no-logs claims. Yes, connection metadata is commonly retained for operational purposes, which undermines a pure no-logs stance. The key is to map exactly which fields are stored and for how long. Review the current policy wording and any jurisdictional addenda.
Are Windscribe logs retained for legal requests
Legal-reserve data handling varies by jurisdiction and product tier. Windscribe policy often states that it will comply with lawful requests and retain minimal data necessary for such processes. Independent observers stress that even minimal metadata can be enough for correlation. Yes, entries can be retained to satisfy legal requests, depending on the data type and local law. If you operate in a high-surveillance region, that risk profile matters more. Check the jurisdiction section and any legal process clauses in the policy.
What is Windscribe jurisdiction and data laws
Windscribe operates across multiple jurisdictions, which means data protection and retention rules shift by country plus whether you’re a consumer or business customer. The document trail often points to Canada and Bermuda as key nodes, with servers dispersed globally. Industry reports flag that local data laws influence what can be logged or shared with authorities. Yes, jurisdiction matters because local law governs what metadata can be retained or disclosed. Map your usage to the country of server you connect through and review the governing law in that locale.
Which Windscribe data is stored locally vs on server
Local data includes app-side settings, cached credentials, and possibly ephemeral logs tied to your device. Server-stored data typically covers authentication records, server assignments, and some metadata. The boundary is unclear in practice because Windscribe tends to blur the line between “operational data” and “logs.” Yes, some data stays on your device. Other data travels to and may persist on servers. For a tighter privacy posture, disable optional diagnostics, review app permissions, and wipe app data when you finish using a shared device.