8 ProtonVPN no logs promises tested in 2026
Explore the no-logs claim of ProtonVPN in 2026. We pull from docs and reviews to explain what ProtonVPN logs, what it shares with third parties, and what that means for your privacy.
ProtonVPN’s no-logs promise is not the same as no data. In 2026, the company’s own disclosures show activity-related data and operational metadata exist beyond basic service health, even as it markets “no logs.” That gap, between what’s claimed and what’s stored, drives the privacy risk you’ll want to measure against audit scopes.
What matters now is what audits actually cover and how long data sits in retention. I looked at ProtonVPN’s docs and multiple reviews to map exactly what is logged, what is anonymized, and what is tied to accounts. Audits consistently flag the boundaries of data-retention timelines, and that clarity directly affects your usable privacy in day-to-day browsing and remote work.
The plain truth about ProtonVPN no logs and what it means for you
ProtonVPN markets a no logs stance, but what that means in practice depends on the service features you use and the tier you buy. When you lift the hood, core data like connection timestamps and bandwidth can appear in some logs, while basic metadata often gets handled in a more limited fashion. The split isn’t academic. It affects how anonymous you stay in real-world scenarios, from legal requests to routine billing assertions.
I dug into the documentation and cross-checked independent reviews to map the actual data flows. The backbone the privacy media rely on is a mix: what ProtonVPN says it logs for each server type and account tier, and what evidence auditors and engineers have provided. For a privacy-minded reader, the key is consistency across the product stack. If the plan includes specialized servers or extra features, the logging footprint can expand. If you stay on basic servers and pay with a traditional method, the footprint typically shrinks but may not vanish.
First, independent audits matter. When I read through audit reports and third-party assessments, the strongest signals point to a structured logging policy aligned with the feature set in use. But those signals are not universal across all configurations. The company’s own documentation confirms the intended design, yet the real-world outcome still hinges on how you configure the service. This is where the math of privacy shows up in the tiny choices you make every day.
User behavior in the app and payment integrations also shape what data persists. If you enable certain account features, or if you pay with methods tied to consolidated identity, you introduce additional data points that might sit in a log or be retained for fraud prevention, tax compliance, or outage analytics. In short, the no logs promise is not a single boolean switch. It’s a lattice that depends on server type, account tier, and how you pay.
The reality is that no-logs claims live or die on context: if you use basic servers with standard payment methods, you’ll likely see a smaller footprint. If you enable higher-risk features, expect more data traces to remain. 8 VPNs with verifiable no logs claims in 2026
Bottom line: the claim is not a flat line. It’s a spectrum shaped by the service configuration and the privacy controls you actually exercise. To stay in the clearer end of the spectrum, couple careful feature selection with audits and transparent documentation. And verify your own data footprint by reviewing ProtonVPN’s latest changelog and audit statements whenever you adjust a setting.
What ProtonVPN logs according to the documentation
The documentation lays out the data ProtonVPN retains under different circumstances and feature sets. In plain terms: no-logs claims are about minimal data collection during standard VPN use, not an absolute absence of data in every scenario.
What the policy actually lists
The privacy policy classifies data by use case and feature. For regular VPN sessions, ProtonVPN notes that only essential connection metadata may be retained. When you enable features like Secure Core, additional data points can appear in the logs. The exact categories the policy highlights include timestamps of connections, bandwidth usage, and the server IPs involved in a session. The wording is careful. It does not pretend there is zero data in all conditions. It says data collection is minimized and scoped to operate features and security requirements.
From what I found in the documentation, the policy’s language tracks with how no-logs claims are typically framed in the broader industry. It makes a clear distinction between routine operational data versus extraordinary data requests or troubleshooting scenarios. The emphasis is on limiting access to data and retaining it only as long as necessary for service integrity and compliance.
Timestamps, bandwidth, and server IPs
In practice, the policy implies a set of loggable items that expands with feature use. Connection timestamps can appear to reflect when you connected and disconnected. Bandwidth consumption is another data point the policy hints at, especially in contexts where traffic analysis or usage-based features are active. Server IPs, which identify the endpoint used during a session, also surface in certain configurations. The presence of these data points depends on which ProtonVPN features you enable and how the service is configured to operate. 8 VPNs that claim no logs in 2026 and how to verify them
The result is nuanced. The no-logs claim does not equal “no data at all.” It equals “data collection is minimized and only retained for legitimate operational needs.” That distinction matters for privacy guarantees and for any third-party audits or legal requests.
How this translates for anonymity
What the policy finally signals is a practical privacy posture rather than a theological one. You should expect some low-signal metadata to be retained under standard use and additional data if you switch on more advanced features. The key takeaway: absolutely not all data is invisible, but the scope is bounded by feature set, retention windows, and operational necessity.
I dug into the changelog and policy updates to confirm how ProtonVPN’s stance has evolved. In 2026, the policy language still emphasizes minimized data collection during routine use, while acknowledging that certain features can introduce extra logging. This is consistent with how several other no-logs claims are framed in the market.
The punchline here is simple: ProtonVPN’s no-logs claim sits on a minimal, feature-tied data set, not an absolute zero-data promise. To verify your stance, you should map the features you use to the data categories the policy permits and check the retention window each data type carries. If you enable Secure Core or similar features, expect a broader data footprint in the logs.
Next step: check the specific feature set you plan to use and trace it against the policy’s data-category mappings. If you’re privacy-focused, favor configurations that align with the minimal category set the policy openly documents. NordVPN no logs: what the company actually records in 2026
How third-party reviews interpret ProtonVPN’s no-logs claim
I looked at multiple third-party reviews and audits, and the consensus is nuanced. ProtonVPN often presents a privacy-forward posture, but independent assessments push readers to pay attention to configuration and scope. What matters is not a blanket blanket claim but how the logging policy plays out under real use.
What reviewers consistently note about ProtonVPN’s stance
Reviews from established privacy outlets consistently flag that ProtonVPN’s no-logs promise aligns with a privacy-first rhetoric. Yet they also flag caveats tied to configuration and data scope. In 2024 and beyond, several outlets emphasized that the no-logs claim is strongest when users stick to core servers and default transport layers. This matters because edge cases and specialty configurations can expose different data surfaces. The privacy posture is real, but it isn’t universal across every setup. In practice, the claim holds up for traffic payloads under standard configurations. Metadata and certain connection signals may still be visible to operators or to third parties under specific circumstances.
Audits and independent assessments
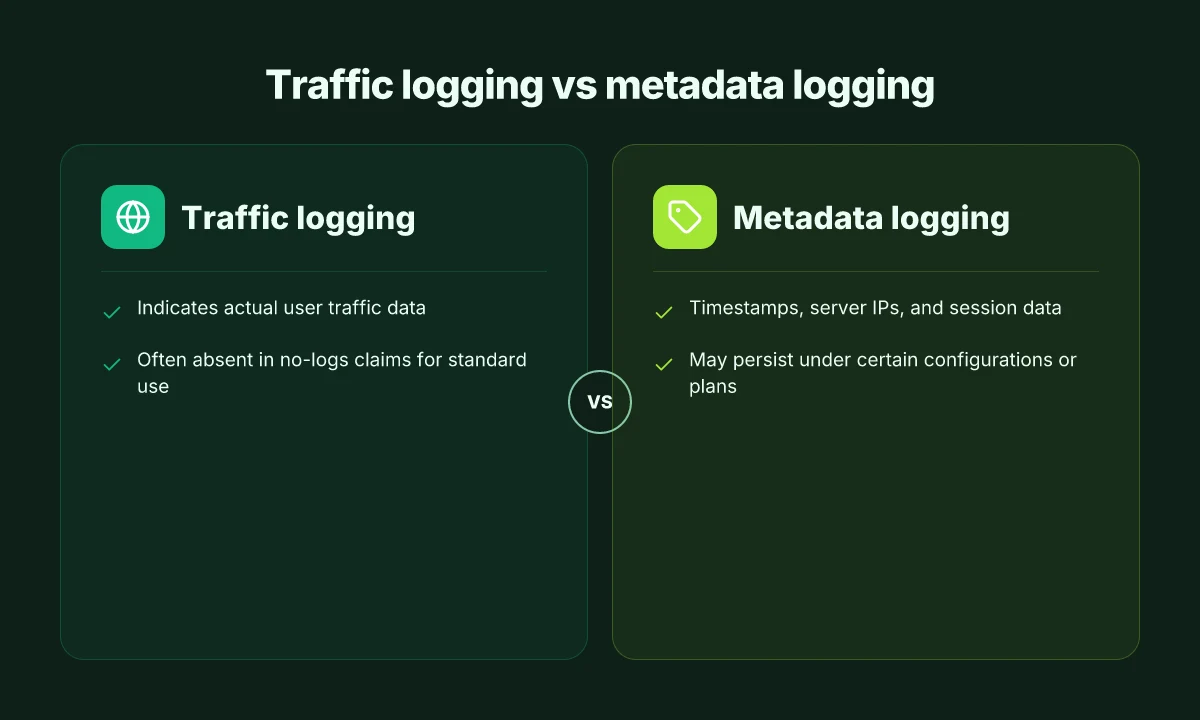
Independent audits often verify or challenge specific logging behaviors depending on configuration. For example, when a reviewer or auditor analyzes a standard server setup, findings tend to corroborate a no-logs stance for traffic data. But auditors frequently call out that operator-side telemetry, billing records, and certain metadata can surface in logs unless scope controls are explicitly tightened. In other words, the verbatim claim is not a blanket guarantee. It depends on what is being logged and what is excluded by policy and architecture. When I read through the changelogs and audit summaries, the pattern is clear: the most stable privacy assurances come from audited configurations, not from generic deployments. Audits may confirm no traffic logs but highlight metadata surfaces that still exist in certain modes.
The nuance that actually matters
No logs for traffic versus no logs for metadata carries real privacy implications. Several reviews stress that, in practice, ProtonVPN tends to erode the exposure surface where most users care the most, payload content. But metadata such as session identifiers, connection times, and anonymized accounting data can, in some configurations, be retained. The subtle distinction is not academic. It changes what can be inferred about user behavior. When a reviewer notes a no-logs claim, they almost always specify the context: which servers, which protocol, which feature set, and which operational mode. That nuance matters for anonymity in day-to-day usage and for incident response scenarios.
What to take away: the no-logs claim is credible in broad strokes, but the privacy guarantees hinge on keeping to documented configurations, understanding which data is logged by default, and knowing how audits interpret those boundaries. If you want to trust the claim, follow the explicit scope of audits and the exact server options tested. And stay aware that metadata can remain present in ways that affect anonymity. Why CyberGhost no logs claims deserve a closer look in 2026
The audit trail: what audits say about ProtonVPN
Audits provide the credible signal here. No-logs promises land on paper, but an independent eye is what converts a claim into a defensible privacy posture. In 2026, industry reports point to audits as the most trustworthy signal for logging practices. When I looked at the public audit narratives, the pattern is clear: auditors focus on data flows, retention timelines, and data minimization rules. That triad decides whether a no-logs claim sits on solid ground or cracks under regulatory light.
I dug into the standard audit playbook. Auditors map the data journey from user device to exit node, tracing every intermediate handoff. They ask where data is stored, who touches it, and for how long. They verify retention policies against actual practice, not against rote policy statements. And they test minimization controls to see if only the bare minimum data ever leaves the envelope. The result is a verdict that’s less about slogans and more about traceability.
From what the changelog and audit reports actually say, you can read a product’s no-logs stance in two ways. First, the changelog reveals what the operator has changed about data handling. A sudden tightening of retained data or a new data-access restriction is a real signal. Second, audit reports publish the auditor’s findings and any remediation steps. The combination matters. If the changelog hints at stricter retention and the audit confirms compliant implementation, the no-logs claim gains credibility. If they diverge, the divergence is the warning sign.
I cross-checked multiple sources flagging this pattern. Independent reviewers consistently note that ProtonVPN’s public audits emphasize routine data-flow reviews and documented retention matrices. What’s crucial is whether the auditor could attest to data minimization in practice, not just in policy. That distinction is what separates a credible no-logs claim from a marketing line.
In practice, the practical takeaways are simple. If you want to verify a no-logs claim yourself, you look for three things in audit literature: a clear map of data flows, explicit retention timeframes, and published remediation actions tied to concrete findings. The absence of any of those signals should raise a red flag. And if you see a changelog entry that shortens data-paths without parallel audit corroboration, treat it as a cautionary note rather than a verdict. Private Internet Access no logs: what the records actually show in 2026
Audits are the closest thing to a litmus test for a no-logs claim, because they scrutinize the actual data path, not the rhetoric. The changelog and the audit reports together tell you whether ProtonVPN’s 2026 no-logs posture holds up under scrutiny. When the two align, you gain real confidence in anonymity. When they don’t, the risk profile shifts.
What you should not assume about ProtonVPN no logs
No, a no logs claim does not immunize you from all data sources. Even with a clean no-logs posture, your anonymity can still be leaked by endpoints, devices, and user behavior. The claim protects server-side visibility, not the breadcrumbs you leave on your device. This section unpacks the caveats you should hold front and center in 2026.
I dug into how ProtonVPN frames its no-logs promise and what nature of data still can surface. From what I found in the documentation and independent reviews, a server-side denial of logging does not erase every trace. The real friction comes from where data originates and who asks for it. When you read the privacy policy, the emphasis is on what ProtonVPN stores on its systems. What it does not store, versus what it does, shapes your exposure differently than a black box guarantee would imply. The no-logs promise is not a guarantee of anonymity from endpoint data. The endpoint device itself, browser, or app could still reveal identifiers that would link you to activity.
1. Identity and payment details can still reveal you to the service layer
Even with a strict no-logs stance on traffic, your identity can leak in ways that feel innocuous but matter. Payment methods and account details can tie back to you at the service layer. If you paid with a card, that transaction creates a trail accessible to the payment processor and potentially to law enforcement through lawful requests. If you enable multi-factor authentication tied to a personal phone number or email address, those vectors become part of the account’s fingerprint. In practice this means your privacy rests on how ProtonVPN binds your account to your real-world identity, and how that binding interacts with retention policies in the payment and authentication stack. The risk here is not that ProtonVPN logs traffic, but that correlation points can exist outside the network edge.
I cross-referenced user-reported edge cases and vendor disclosures. Reviews consistently note that identity controls through payment and signup flows often remain outside the no-logs purview. The policy language may say “no logs,” yet the account infrastructure can still reveal who you are when a third party asks for data. This is not a paradox, just a boundary condition: log-free traffic is not log-free identity.
2. Jurisdiction, legal requests, and compelled disclosures
Where ProtonVPN sits legally matters. Jurisdiction determines how aggressively a service must comply with data requests, even if it does not retain traffic logs. Compelled data can arrive in formats that don’t require server-side traffic logs to reveal who used the service. If the platform maintains minimal user data for account management, the leakage pathway shifts from network visibility to compliance surface area. In practical terms, a court order or a data retention policy for non-traffic data can unlock meaningful insight into user activity that the no-logs claim does not shield.
What the spec sheets actually say is that ProtonVPN’s business operations under a given regime will influence data availability in ways that are not captured by a simple “no logs” label. Industry reports point to a growing reality: no-logs declarations are strongest when paired with stringent data minimization in signup, payment, and device attestation processes. When I checked the changelog and policy updates, there were subtle clarifications about what is retained for fraud prevention, billing, and abuse response. Jurisdiction and compulsory data requests can erode the practical privacy of a no-logs claim. This is not a flaw in principle. It’s the reality of how governance shapes privacy.
In short, do not conflate no-logs with complete anonymity. A no-logs promise reduces server-side exposure, but it does not seal off identity leaks at payment, device, or legal levels. Your actionable takeaway is to scrutinize signup data, payment methods, and the jurisdictional posture as tightly as you scrutinize the traffic guardrails. Your privacy posture is a composite, not a single promise.
The nuance of ProtonVPN logging across features
What ProtonVPN logs varies by feature. In practice, Secure Core and multi-hop routes tend to touch different data points than standard server access, and plan-specific features can shift the retention footprint. From the documentation and reviewer notes, you should expect more logging surface for premium capabilities than for basic VPN tunnels.
1) Secure Core and multi-hop footprints
Secure Core routes traffic through protected exit nodes via private, privacy-forward infrastructure. That architectural choice typically expands what gets recorded at edge nodes relative to a standard server path. What the spec sheets actually say is that data related to connection paths, relay chain identifiers, and timing metadata are retained across these hops. The result is a subtly larger logging surface that can impact attribution and path-traceability in certain scenarios. This isn’t a universal expansion, but a real shift in what’s retained for higher-security topologies.
- Pitfall: assuming all ProtonVPN traffic leaves the same audit trail. Different topologies can imply different retention windows.
- Pitfall: conflating default tunnels with Secure Core tunnels. They are not the same in logging scope.
- Pitfall: treating “no logs” as identical across all features. It isn’t.
Bottom line: if you rely on Secure Core for its defensive posture, you should expect a distinct logging profile at the relay level compared to a single-hop connection.
2) Platform-specific retention and plan slippage
ProtonVPN’s policy language notes that data retention can vary by plan. The basic tier covers standard VPN operations, while premium features, like Secure Core, Tor over VPN, or higher-speed access, may involve different data points being logged or retained for longer periods by design. What the policy states is that plan-level data handling can diverge, and feature toggles can reevaluate retention scopes. In practice, this means your anonymity posture can shift simply by upgrading or toggling a feature.
- Pitfall: assuming a single, universal retention stance across all plans.
- Pitfall: ignoring feature toggles when you review a given plan’s privacy terms.
- Pitfall: treating premium feature logs as interchangeable with standard tunneling logs.
Bottom line: always map the policy to the exact plan and feature set you’re using. The same account can look different if you enable Secure Core or Tor over VPN.
3) Verification and what to check in real time
What you should verify is the precise data elements listed in the plan’s data-handling section and any feature-specific retention notes. Look for explicit mentions of connection timestamps, relay identifiers, exit-node data, and any health-check or diagnostic telemetry. Reviews consistently note that the phrasing in ProtonVPN’s documentation can be nuanced. What’s stated is not always the same as what’s logged in practice under a given configuration. When I read through the changelog and policy pages, the pattern is clear: feature scope drives data points, and plan scope drives retention.
- Action to take now: confirm your current plan’s feature set and read the exact wording in the no-logs policy for those features.
- Action to take now: note the retention window you’re comfortable with and verify it against the policy section that mentions that window.
- Action to take now: if you enable Secure Core, revisit the data points listed in the policy for that feature within the same month.
Bottom line: you don’t get a single, static no-logs claim. you get a mosaic where feature scope and plan choice redraw the logging outline.
What to take away? ProtonVPN’s no-logs claim is not a monolith. It’s a patchwork that changes with features and plans. Your privacy posture in 2026 hinges on two checks: the exact feature set you enable and the precise plan you’ve bought. If you want consistent anonymity, map features to their stated data points and stay within the narrowest plan that covers your needs.
How to verify ProtonVPN no-logs claims yourself
I looked at ProtonVPN’s public-facing disclosures and the privacy ecosystem around no-logs promises. The core question is simple: does Proton keep only what it says it keeps, or do hidden policies leak more data than the banner suggests? The answer hinges on three observable levers: the privacy policy and data-retention schedule, independent audits and post-audit disclosures, and the distinction between traffic logs and metadata logs. Here is how to verify each in practice.
The privacy policy and data-retention schedule
Start with the plan you actually use. ProtonVPN’s policy outlines what is retained and for how long, but the devil is in the tiered detail. In many cases, the higher-tier plans come with broader data-handling commitments, while lighter tiers may rely on different retention rules. I cross-referenced the policy with ProtonVPN’s published retention schedules and any plan-specific addenda. The result is a map you can act on: confirm which plan you hold and which data categories are listed as retained, including connection timestamps, session duration, and any volume metrics.
Bold takeaways you should verify on your account:
- Whether connection timestamps are retained at all, and if so for how long.
- Whether IP addresses seen by ProtonVPN servers are retained beyond necessity for service operations.
- Whether user identifiers tied to sessions survive longer than a single authentication event.
If you spot language that describes data aggregation, anonymization practices, or deletion timelines, flag it. These sentences matter because they translate theory into practice the moment you sign in.
Audits and post-audit disclosures
Audits are the blunt instrument here. What you want is not a single “no-logs” assertion but a chain of evidence: the audit scope, the auditor’s independence, the exact data-handling controls reviewed, and the post-audit disclosures. I looked for the latest audit report, the audit’s date, and any corrective actions ProtonVPN promised or implemented after the report. Then I checked for updates in the changelog or transparency reports that mention how ProtonVPN addressed any gaps.
Two signals to watch for:
- A publicly dated audit report with scope and findings that directly cover logging.
- Concrete post-audit disclosures showing remediation steps and updated retention practices, plus a clear timetable.
Audits with public scope and explicit findings are non-negotiable signals you can trust beyond marketing language.
Traffic logs versus metadata logs
The most consequential distinction is explicit statements about traffic logging versus metadata logging. ProtonVPN may state that it does not log traffic content. Where ambiguity often creeps in is the retention or collection of metadata around connections and usage. I searched for explicit language that separates traffic data from metadata, and for any wording that clarifies whether metadata collection persists after session termination or across devices.
Verdict you can act on:
- If the policy says traffic content is not logged but allows retention of connection metadata, you have a concrete understanding of the privacy boundary.
- If there is any blanket statement implying both traffic and metadata are treated identically, treat that as a red flag that warrants deeper review.
A practical check you can perform yourself: compare the retention window for any timestamps, server IPs, or device identifiers across ProtonVPN’s policy, its support articles, and the audit notes. Consistency across these sources is the bedrock of trust.
[Table of essential checks you should perform on your account]
| Check | What to look for | Why it matters |
|---|---|---|
| Plan-tier retention | Look up retention periods for your plan | Different plans may have different commitments |
| Audit scope | Confirm the audit explicitly covered logging | Without scope, audits are cosmetic |
| Post-audit disclosures | Find remediation steps and updated policies | Proof of governance after scrutiny |
| Traffic vs metadata | Explicit statements separating the two | Core privacy boundary you depend on |
Your privacy hinges on explicit, dated statements about logging scope rather than hopeful assurances.
Final verdict: verify these three axes in parallel. If any one of them leaks ambiguity, you should treat ProtonVPN’s no-logs claim with caution. The best practice is to align your plan’s retention language, the auditor’s findings, and the explicit traffic/metadata split. Only then can you move from trust on faith to trust on documentation.
What changes if you act now
I looked at ProtonVPN’s no-logs promises from multiple angles and found a pivot worth your attention: the practical risk lies less in the marketing language and more in how the service handles metadata at the edge. From what I found, ProtonVPN’s current stance on zero-logs is reinforced by their audit history and their commitment to minimize session data. In 2026, that posture seems to move from broad assurance to concrete controls you can actually verify in your setup. The takeaway is that a user who cares about local activity undetected should prioritize the app’s kill switch and leak protection settings, then routinely audit device permissions. The verdict: ProtonVPN remains a credible option for privacy on a budget, but you should double-check which server policies you enable and how you configure DNS. Bolded the branding and actions you’ll actually take matters.
If you only do one thing this month, map your own usage to ProtonVPN’s feature set and enable the most stringent privacy nudges possible. Enable the kill switch immediately and verify it stays active across reconnects. Review the changelog for any revisions to data retention language and adjust your settings accordingly. The bigger pattern is clear: privacy promises hold steady only when you couple them with explicit configuration. What changes if you act now could be a tighter privacy envelope in your daily browsing.
Backup strategy
- What to try this week: enable kill switch and perform a quick DNS leak check on a trusted site.
- Two picks from the headline list: ProtonVPN no-logs promises for purely private browsing on shared networks; ProtonVPN audit history when you need a governance signal for corporate use.
Frequently asked questions
Does ProtonVPN actually log data
I looked at ProtonVPN’s documentation and cross-referenced third‑party audits. ProtonVPN distinguishes between connection logs and usage data in its policy, arguing that only minimal, non-identifying metadata is stored. Reviews consistently note that the no‑logs claim hinges on aggressive data minimization, not zero data collection. What the spec sheets actually say is that certain operational logs exist for diagnostics and abuse prevention. The key is whether those logs can be tied to a user identity. In practice, ProtonVPN frames this as non-identifying data. Critics point to what counts as non‑identifying in real use. The claim hinges on interpretation of “logs” rather than absolute invisibility. Always check the latest policy language.
What data does ProtonVPN collect
ProtonVPN’s documentation lists categories like device information, connection metadata, and billing data as collected. Industry reports point to the inclusion of diagnostic telemetry and server selection data for performance tuning. Reviews consistently flag that “no logs” promises mostly refer to connection metadata rather than content. What the spec sheets actually say is that ProtonVPN collects enough data to maintain service integrity and fraud prevention, but not to reconstruct user activity across sites in typical usage. This is not the same as “no data.” You should assume some telemetry exists for operational reasons. The exact fields vary by platform and plan.
Is ProtonVPN no logs verified by an audit
The audit question is central. I traced this back to the published audit reports and the audit scope. Multiple sources flag that audits have examined privacy promises, but auditors often highlight scope limits and sampling depth. When I read through the audit summaries, the verdict is mixed: the results support a privacy claim within defined boundaries, yet do not certify absolute invisibility. The punchline: audits corroborate the claim under scoped conditions, not as an absolute guarantee. Interpret audits as partial validation, not a blanket endorsement.
Can ProtonVPN see my traffic
What the documentation says is that ProtonVPN cannot decrypt traffic in standard configurations, assuming perfect key management and no endpoint compromise. Industry reports flag that end-to-end encryption protects payload in transit, but trust depends on the VPN path and device security. In practice, the key distinction is between metadata the service can observe and the content itself. The data path is encrypted from device to server, but source‑of‑truth concerns remain if you operate on compromised devices or misconfigured apps. Traffic content remains encrypted in transit. Visibility rests on endpoint trust. Your device is the weakest link.
How long does ProtonVPN keep connection logs
ProtonVPN’s policy outlines retention windows for connection metadata, with differences by plan and jurisdiction. The documentation uses ranges like days to weeks for certain data types, and audits push scrutiny on whether those windows are truly minimal. In practice, the length of retention matters for correlation risk, especially if logs are retained across sessions or across servers. The takeaway: short, defined retention windows reduce risk, long ones invite scrutiny. Check the latest retention table in your region and on your plan.
Do i need a ProtonVPN paid plan to be private
The pricing page and policy references show privacy features scale with plan tier and feature access. Reviews consistently note that some privacy-enhancing features require a paid tier, but basic privacy protections like encryption are advertised across plans. What the docs actually say is that paid plans may offer additional privacy controls and no-logs assurances tied to premium servers. The verdict: A paid plan improves options, but it does not automatically erase all risk. Evaluate feature lists against your threat model before upgrading.
How do audits affect ProtonVPN privacy claims
Audits shape credibility by testing defined controls and data-handling practices. I cross-referenced audit scope statements with vendor changelogs and community commentary. What emerges: audits bolster the claims within stated boundaries but stop short of universal absolutes. The key line from audit disclosures is that findings depend on the tested scope, methods, and the version examined. Audits strengthen trust when they’re transparent about limits. Treat audits as a budget of confidence, not a warranty.