How to embed certificates in your openvpn ovpn configuration files: A practical guide for secure VPN setups
How to embed certificates in your openvpn ovpn configuration files Quick fact: embedding certificates directly into your .ovpn file simplifies deployment and reduces the risk of misplacing certificate files on client devices.
If you’re setting up OpenVPN and want a clean, portable client profile, embedding the certificates and keys inside the .ovpn file is a solid approach. This guide walks you through the why, the how, and the best practices with step-by-step instructions, practical tips, and common pitfalls to avoid.
What you’ll learn
- Why embedding certificates can simplify client distribution
- What you need before you start certificates, keys, and config files
- Step-by-step walkthrough to embed CA cert, client cert, client key, and TLS key ta key
- How to verify and test your embedded configuration
- Security considerations and best practices
- Troubleshooting common issues
- Additional tips for automation and large-scale deployments
Useful resources to get you started Apple Website - apple.com Artificial Intelligence Wikipedia - en.wikipedia.org/wiki/Artificial_intelligence OpenVPN Documentation - openvpn.net/docs/ TLS Key Exchange - en.wikipedia.org/wiki/Transport_Layer_Security VPN Security Best Practices - nist.gov OpenVPN Community Forums - community.openvpn.net DNS Leak Test - dnsleaktest.com Certificate Authority Guide - cacert.org
Tables to compare prerequisites and preparation steps
| Item | Required? | Notes | Typical format | Example |
|---|---|---|---|---|
| OpenVPN server TLS setup | yes | tls-auth or tls-crypt recommended | config on server | tls-auth ta.key |
| CA certificate | yes | PEM format | ca.crt | Included in file |
| Client certificate | yes | PEM format | client.crt | Included in file |
| Client private key | yes | PEM format | client.key | Included in file |
| TLS key (ta.key or tls-crypt) | optional | for tls-auth/ tls-crypt | ta.key or tls-crypt.key | Included when used |
Compiled November 2026; check the provider's site for current details.
Why you might want to embed certificates in a single .ovpn file
- Portability: A single file is easier to send to users and deploy across devices.
- Reduced file management: No need to keep track of separate certs and keys on each client.
- Fewer misconfigurations: Minimize the chance of pointing the client to the wrong certificate file path.
However, embedding also has trade-offs. If you frequently rotate certificates, you’ll need to update and redistribute the entire .ovpn file. It’s also crucial to protect the embedded data with appropriate file permissions and access controls.
What you’ll need before you begin
- OpenVPN server configuration that already uses TLS authentication tls-auth or tls-crypt.
- CA certificate ca.crt or a CA-signed chain.
- Client certificate client.crt and client private key client.key.
- Optional: tls-auth or tls-crypt static key ta.key or tls-crypt.key.
- A text editor and a basic familiarity with PEM format certificates and keys.
- The base OpenVPN client configuration template client.ovpn or a fresh one.
Typical PEM blocks you’ll work with
- CA certificate: -----BEGIN CERTIFICATE----- … -----END CERTIFICATE-----
- Client certificate: -----BEGIN CERTIFICATE----- … -----END CERTIFICATE-----
- Client private key: -----BEGIN PRIVATE KEY----- … -----END PRIVATE KEY-----
- TLS key ta.key: -----BEGIN OpenVPN Static key V1----- … -----END OpenVPN Static key V1-----
Step-by-step: embed the CA cert, client cert, and client key
- Start with a clean OpenVPN client template
- Use your existing client.ovpn as a base, or create a new file named client.ovpn.
- Ensure the file contains the essential directives: client dev tun or dev tap depending on your setup proto udp or tcp remote your.vpn.server 1194 resolv-retry infinite nobind persist-key persist-tun ca ca.crt cert client.crt key client.key tls-auth ta.key 1 if you’re using tls-auth cipher AES-256-CBC verb 3
- Remove separate certificate/key file references
- You will embed the contents inside the same file, so remove the lines: ca ca.crt cert client.crt key client.key tls-auth ta.key 1 if applicable tls-crypt tls-crypt.key if applicable
- Create embedded sections in the correct order
- Place the PEM blocks below the global config, using tag-like sections for readability. The order is:
paste CA certificate here paste client certificate here paste client private key here Optional TLS keys:paste ta.key here Or for TLS crypt:paste tls-crypt.key here
- Place the PEM blocks below the global config, using tag-like sections for readability. The order is:
- Example of a fully embedded .ovpn block
omit this header when you paste into your file; this is just illustration
Client dev tun proto udp remote vpn.example.com 1194 resolv-retry infinite nobind persist-key persist-tun cipher AES-256-CBC verb 3
- Save and secure the file
- After embedding, save the file with a .ovpn extension.
- Set restrictive file permissions to prevent other users from reading sensitive material, for example: On Unix-like systems: chmod 600 client.ovpn
- If you’re sharing, use secure channels and consider encrypting the file when stored on disk.
- Validate the embedded file
- OpenVPN GUI or CLI should be able to load the embedded .ovpn file without additional certificates on disk.
- Ensure that the server can be reached and that the VPN connects successfully.
- You can test by launching the client and watching logs for any certificate or TLS handshake errors.
Step-by-step: embed the TLS key ta.key or tls-crypt key if used
If you’re using tls-auth ta.key
- The ta.key is a shared secret added for TLS authentication. When embedding:
-----BEGIN OpenVPN Static key V1----- 4f2a...ta.key content... -----END OpenVPN Static key V1-----
If you’re using tls-crypt tls-crypt.key Estensione browsec vpn per microsoft edge guida completa e recensione 2026
- The tls-crypt key is used to provide additional encryption for control channel. When embedding:
-----BEGIN OpenVPN Static key V1----- ...tls-crypt.key content... -----END OpenVPN Static key V1-----
Note: If you’re only using TLS with a client certificate and require no tls-auth, you can omit the TLS key sections entirely.
Best practices for embedded OpenVPN profiles
- Keep a clean separation in your template: always start from a solid base file with correct directives, then add embedded blocks.
- Use distinct names for your client certificates if you manage multiple users or devices to avoid accidental cross-use.
- Consider automating the embedding process with a small script that reads PEM files and outputs a single .ovpn file. This reduces human error and speeds up mass deployments.
- Rotate certificates on a predictable schedule and have a versioning system on your embedded profiles.
- For enterprise deployments, use hardware-backed keys where feasible and enforce MFA for distribution access.
Tables to compare step-by-step embedding process
| Step | Action | Output | Key directive adjustments | Notes |
|---|---|---|---|---|
| 1 | Start with clean template | client.ovpn | remove external ca/cert/key references | Use base directives |
| 2 | Embed CA cert | within <ca> block | ca ca.crt lines removed | PEM block only |
| 3 | Embed client cert | within <cert> block | cert client.crt lines removed | PEM block only |
| 4 | Embed client key | within <key> block | key client.key lines removed | PEM block only |
| 5 | If tls-auth/ tls-crypt used | embed as <tls-auth> or <tls-crypt> | remove ta. key lines | PEM block or inline |
Compiled November 2026; check the provider's site for current details.
Security considerations when embedding certificates
- Access control: The embedded file contains sensitive data. Restrict who can read it. On Linux, use file permissions; on Windows, set proper ACLs.
- Secure distribution: If you’re emailing or sharing the .ovpn file, use encrypted channels or password-protect the archive.
- Key material exposure: If you suspect a certificate/key is compromised, revoke and replace the certificate, then re-embed into new profiles.
- Least privilege: The VPN user should have only the rights needed for their role. Avoid giving more access than necessary through the VPN.
- Audit logging: Keep a log of distribution and rotation events to track who has which profile.
How to test an embedded .ovpn file
- Basic connection test: Start the OpenVPN client with the embedded file and confirm you establish a tunnel.
- DNS leak check: After connection, run a DNS leak test to ensure your DNS requests aren’t leaking outside the VPN path.
- IP address verification: Check your public IP before and after connecting to confirm routing through the VPN.
- Key/certificate validation: If you see TLS handshake errors or certificate verification failures, re-check the embedded blocks for proper PEM formatting and correct order.
- Server compatibility: Ensure the server supports the cipher and TLS settings chosen in your client configuration.
Common issues and quick fixes
- Problem: “TLS Error: TLS handshake failed” Fix: Verify ta.key or tls-crypt usage, ensure the TLS key is correctly embedded, and that the server uses matching settings.
- Problem: “Could not load certificate” or “Unable to load private key”
Fix: Double-check the
and blocks for correct PEM boundaries and no extra characters or spaces outside the blocks. - Problem: “Cannot allocate TUN/TAP device” on Linux Fix: Ensure you have privileges to create a tun device and that the kernel supports tun/tap. Run with appropriate permissions.
- Problem: “DNS resolution failed after connection” Fix: Confirm DNS server settings in the OpenVPN config and ensure no conflicting resolver configurations on the client.
Tables to compare verification and testing steps
| Test | Method | Expected result | Command example | Notes |
|---|---|---|---|---|
| Basic connectivity | OpenVPN connect | Successful handshake | openvpn --config client.ovpn | Ensure server reachable |
| TLS key presence | Verify inline blocks | All blocks present | grep -E "<ca> | <cert> |
| DNS leaks check | Run DNS leak test | No leaks | dnsleaktest.com | Independent test |
| Authentication | Validate certs | Valid client cert | openssl verify -CAfile ca.crt client.crt | Ensure chain ok |
| Test TLS auth | If used | ta.key accepted | openvpn --config client.ovpn --verb 3 | Confirm ta.key usage |
Compiled November 2026; check the provider's site for current details. No puedes instalar forticlient vpn en windows 10 aqui te digo como arreglarlo y otros consejos de configuración
Workflow tips for teams and automation
- Scriptable embedding: Create a small script Python, Bash, or PowerShell that reads ca.crt, client.crt, client.key, ta.key, and tls-crypt.key, then outputs a single .ovpn file with the correct embedded sections.
- Version control: Store templates and scripts in a secure repository with access controls. Do not commit actual private keys to public repositories.
- CI/CD for profiles: For large teams, set up a pipeline that builds embedded profiles for each user group and distribution channel, then distributes via secure SFTP or a gated download portal.
- Rotation automation: When renewing certificates, implement a process that validates the new PEM blocks and automatically re-embeds them into the appropriate client profiles.
Real-world tips and examples
- If you’re distributing to Windows users, consider adding a quick-start section within the .ovpn file that guides them to install the OpenVPN client and import the embedded profile.
- For macOS and iOS users, test the embedded profile with the OpenVPN Connect app to ensure seamless import and connectivity.
- In remote work scenarios, embed a short note about the VPN’s purpose and the date of the last certificate rotation, so admins and users stay aligned on security posture.
- If you’re using split-tunnel routing, specify the necessary redirect-gateway and route-nopull options accordingly, while keeping the embedded blocks intact.
Tables to compare tips for security and maintenance
| Topic | Recommendation | Impact | Trade-off | Notes |
|---|---|---|---|---|
| File permissions | Restrict access to embed data | Reduces leakage risk | May complicate deployment | Use file permissions carefully |
| Certificate rotation | Update entire .ovpn file | Consistency | Re-distribution required | Plan automation |
| Embedded vs external | Prefer embedding for portability | Fewer misconfigurations | Larger file; harder updates | Balance with rotation needs |
| Access controls | Limit who can edit template | Safer profiles | Admin overhead | Implement checks |
Compiled November 2026; check the provider's site for current details.
Quick-reference checklist
- Base configuration ready client, dev, proto, remote
- PEM blocks prepared ca.crt, client.crt, client.key
- Optional TLS blocks prepared ta.key, tls-crypt.key
- Removed external file references in the config
- Embedded blocks placed in correct order
- File permissions secured
- Tested connection end-to-end
- Rotation and distribution plan in place
| VPN | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|
 NordVPN | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
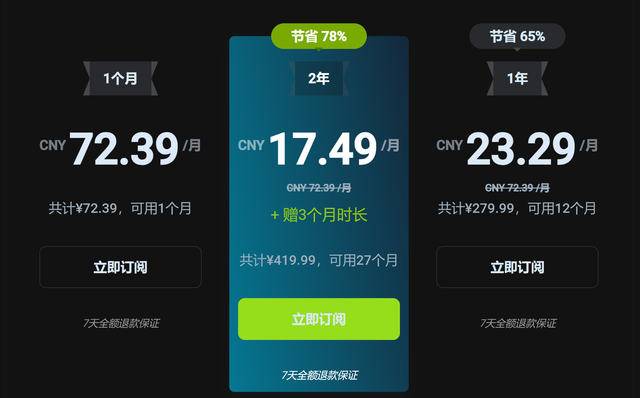
 ZoogVPN | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (2.5 s) | 4.2/5 (195 reviews) |
 ExpressVPN | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✓ Yes (2.5 s) | 2.1/5 (1,040 reviews) |
 Astrill VPN | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ✗ | ✗ | ✓ | ✓ Yes (2.6 s) | 4.4/5 (17,994 reviews) |
 AdGuard VPN | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (2.3 s) | 4.3/5 (290 reviews) |
 Mullvad | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (2.3 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-11 04:07 Beijing time.
Trustpilot score and review count checked 2026-11-10.
FAQ: Frequently Asked Questions
Can I embed certificates into an .ovpn file on Windows, macOS, and Linux?
Yes. The embedded approach works across major platforms. Just ensure the OpenVPN client on that platform supports the embedded blocks and PEM formatting.
Do embedded .ovpn profiles preserve security when shared?
Embedded profiles are as secure as the container file. Protect the file with proper permissions and distribute through secure channels. Avoid emailing raw keys when possible.
What if my server uses tls-auth or tls-crypt?
Include the corresponding
Is embedding certificates better than keeping separate certificate files?
Embedding simplifies distribution and reduces file management errors for many users. However, for large enterprises with frequent certificate rotation, separate management of keys can be more flexible if you have strong distribution controls.
How do I automate embedding for a large number of users?
Build a script that reads the certificate and key files, then outputs a single .ovpn per user with all blocks embedded. Integrate this into your CI/CD pipeline for consistent, repeatable builds.
How can I verify that the embedded content is in the correct PEM format?
Look for proper PEM boundaries:
- BEGIN CERTIFICATE / END CERTIFICATE
- BEGIN PRIVATE KEY / END PRIVATE KEY
- BEGIN OpenVPN Static key V1 / END OpenVPN Static key V1 Verify there are no extra characters or trailing spaces outside the blocks.
What if the embedded file doesn’t connect?
Check for:
- Mismatched server/client TLS settings
- Incorrect or corrupted PEM blocks
- Permissions preventing access to the file
- Firewall or network issues blocking VPN traffic
Are there risks if the embedded .ovpn file is stolen?
Yes. The file contains private keys. Treat it like other sensitive credentials: secure storage, restricted access, and prompt revocation if compromised. Onedrive Not Working With VPN Heres How To Fix It: Quick Steps, Common Issues, And Pro Tips
Should I rotate certificates automatically?
Rotating certificates regularly is a good security practice. Plan an automated rotation workflow that updates the embedded blocks and redistributes the updated profiles to users.
Can I embed multiple client certificates in one .ovpn file?
Typically, no. Each embedded .ovpn profile is intended for a single client certificate and key pair. For multiple users, generate separate embedded profiles per user.
Sources:
How to Add NordVPN to Your iPhone a Step by Step Guide: Quick Start, Setup Tips, and Best Practices
Vpn接続できないルーター設定:原因特定と解決策
英超官网:全面解析、实用指南与最新动态 Come scaricare in modo sicuro su emule con una vpn la guida completa purevpn
The Best VPNs for iqiyi Unlock Global Content Stream Like a Pro
Meilleurs vpn avec port forwarding en 2026 guide complet pour une connexion optimale et performances optimales